 www.theguardian.com
Sainsbury's Suspends Facial Recognition After Wrongful Ejection of Shopper
Article Content

- •Sainsbury's paused facial recognition technology after a wrongful ejection incident.
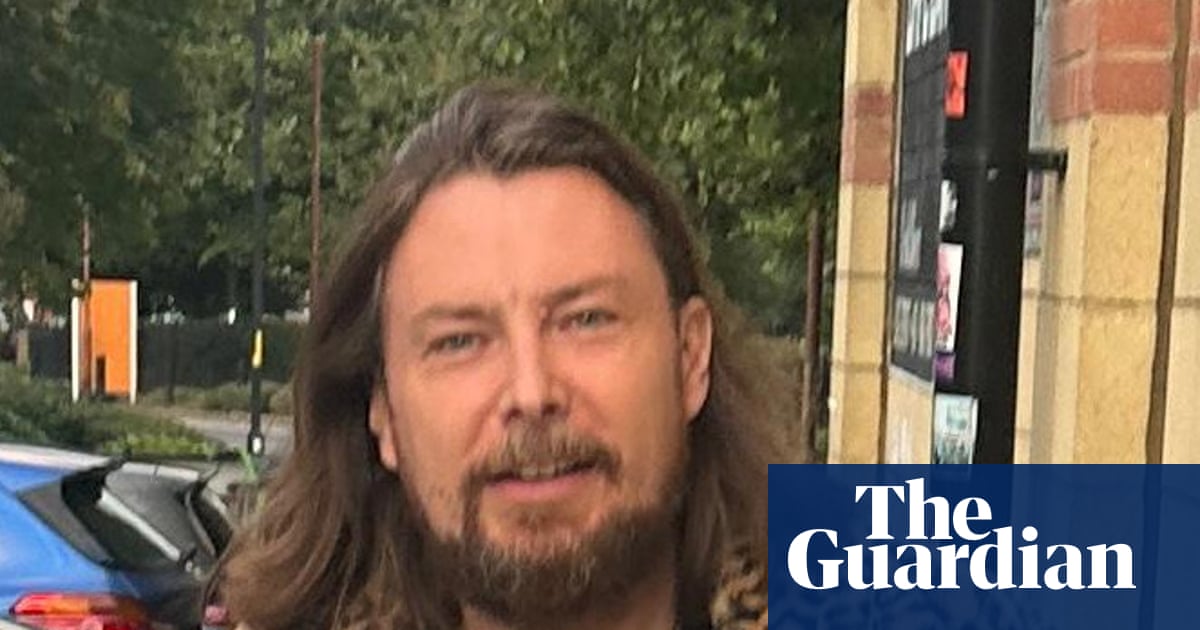
- •Matt Arnold was mistakenly identified as a shoplifter, leading to his ejection from the store.
- •The supermarket claims human error caused the incident, not a flaw in the Facewatch system.
Sainsbury's has temporarily halted its use of AI facial recognition technology at a store in East Dulwich after Matt Arnold, a comedy promoter, was wrongly identified as a shoplifter and ejected. Arnold was approached by store managers while using a self-service checkout and was told he could not be served due to a previous incident. The supermarket chain attributed the error to human mishandling rather than a flaw in the Facewatch system, which claims a 99.98% accuracy rate. This incident follows a similar wrongful ejection earlier this year involving another customer, Warren Rajah. Arnold expressed concerns about the implications of AI technology, particularly for vulnerable individuals. Sainsbury's has apologized to Arnold and is conducting an investigation into the incident. The company has faced criticism for its reliance on facial recognition technology, which has been linked to other wrongful accusations in the past.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…