 Techedt
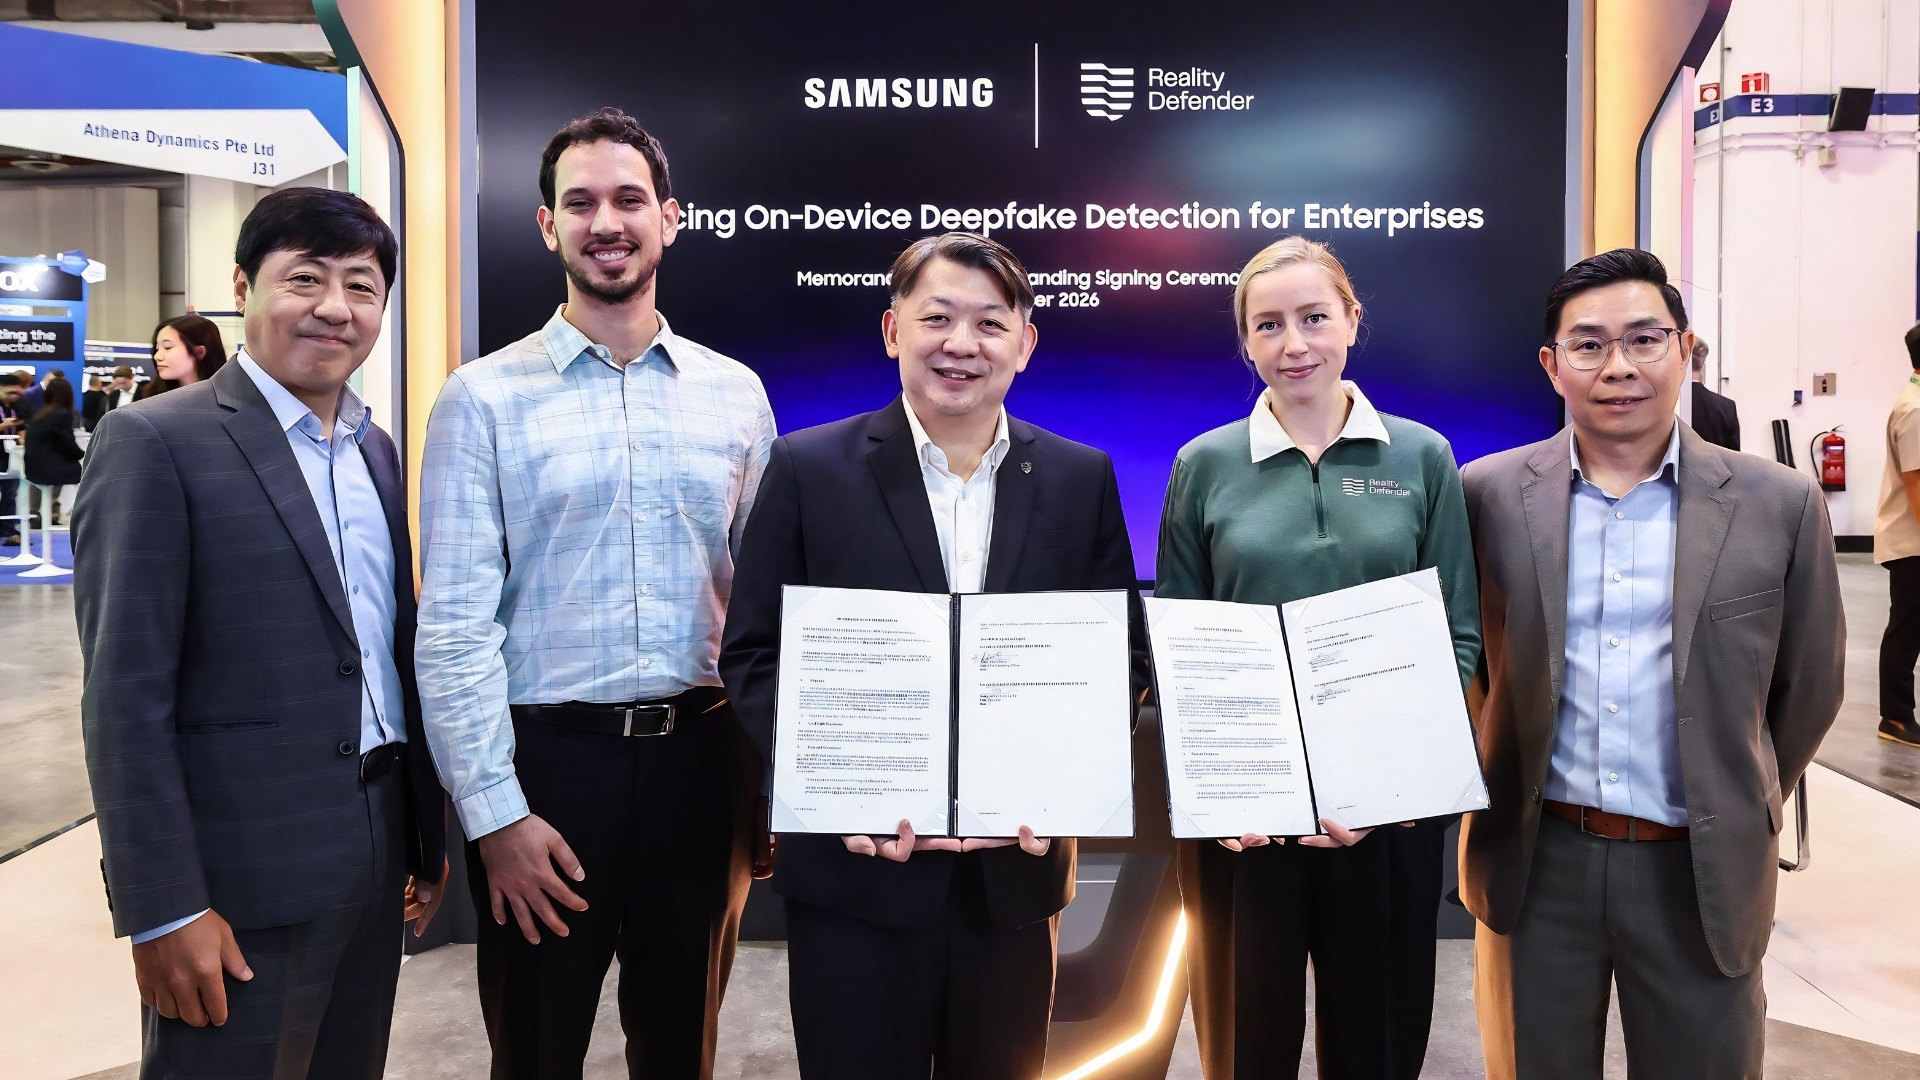
Samsung and Reality Defender Collaborate on Deepfake Detection for Enterprises
Article Content

- •Samsung and Reality Defender are developing deepfake detection for Galaxy devices.
- •56% of Singaporean businesses reported audio deepfake fraud in 2024.
- •The solution will analyze content on-device, enhancing security and privacy.
Samsung Electronics Singapore and Reality Defender have signed a memorandum of understanding to develop an on-device deepfake detection solution for enterprises in Singapore. The technology aims to identify AI-generated voice, video, and images on Samsung Galaxy devices, reducing reliance on cloud services for sensitive data. This initiative comes in response to a 2024 survey indicating that 56% of Singaporean businesses faced audio deepfake fraud, while 52% encountered video deepfakes. In 2025, scams involving impersonation of government officials resulted in losses of at least S$242.9 million. The planned solution will integrate Reality Defender’s detection capabilities with Samsung Knox, enhancing enterprise security by analyzing content directly on devices. The rollout is expected to occur on the Galaxy S26 series and later models. The partnership aims to protect organizations from AI-generated threats and bolster confidence in digital communications.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track Samsung Electronics Singapore in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What devices will support the deepfake detection tool?
What are the main features of this detection solution?
How significant is the threat of deepfakes in Singapore?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…