 Dunyanews.Tv
Samsung Galaxy Z Fold 8 Series Receives October 2026 Security Update
Article Content

- •Samsung's October 2026 update includes 79 security improvements for Galaxy Z Fold 8 and Z Flip 8.
- •The update addresses 62 security issues and is being rolled out globally, starting with Europe and India.
- •The update size for the Galaxy Z Fold 8 Ultra is approximately 537.17MB with firmware version AZIJ.
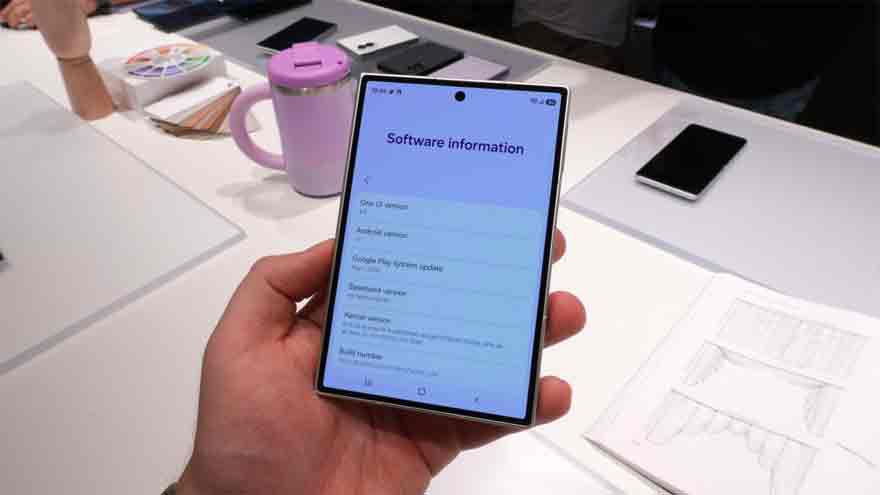
Samsung has begun rolling out the October 2026 security update for the Galaxy Z Fold 8, Z Fold 8 Ultra, and Z Flip 8, which includes 79 security improvements. The update addresses 62 security issues and is being distributed globally, with Europe and India among the first regions to receive it. The update was initially released in South Korea and has a firmware version ending in AZIJ. The update size for the Galaxy Z Fold 8 Ultra is approximately 537.17MB. Samsung's update process allows users to continue using their devices during installation due to SEAMLESS UPDATES technology. The company has not disclosed specific CVEs related to these improvements. The update is part of Samsung's commitment to providing monthly security updates for its devices.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
Which devices are affected by the update?
What security issues does the update address?
How large is the update for the Galaxy Z Fold 8 Ultra?
Continue Reading
 Critical Citrix NetScaler Vulnerabilities Actively Exploited in Finland The National Cyber Security Centre Finland (NCSC-FI) issued an alert regarding critical vulnerabilities in Citrix NetScaler ADC and Gateway products, specifically CVE-2026-88771 and CVE-2026-88772, which are being actively exploited in Finland. These vulnerabilities allow attackers to execute remote code without…
 Critical Authentication Bypass in Rejetto HFS Exploited Within 24 Hours Anthropic's Mythos model identified a critical authentication bypass in Rejetto HTTP File Server (HFS), tracked as CVE-2026-61500, allowing remote code execution. Discovered by Horizon3 researcher Zach Hanley, the flaw was revealed on September 27, 2026, and exploitation began within 24 hours, with attacks traced to…