 Canadianminingjournal
Sandvik Achieves Advanced Cybersecurity Certification for Mining Equipment
Article Content

- •Sandvik achieved IEC 62443-4-1 Maturity Level 3 certification for cybersecurity.
- •The certification confirms systematic embedding of cybersecurity in product development.
- •Sandvik's Intelligent Control Architecture (SICA) supports the certification process.
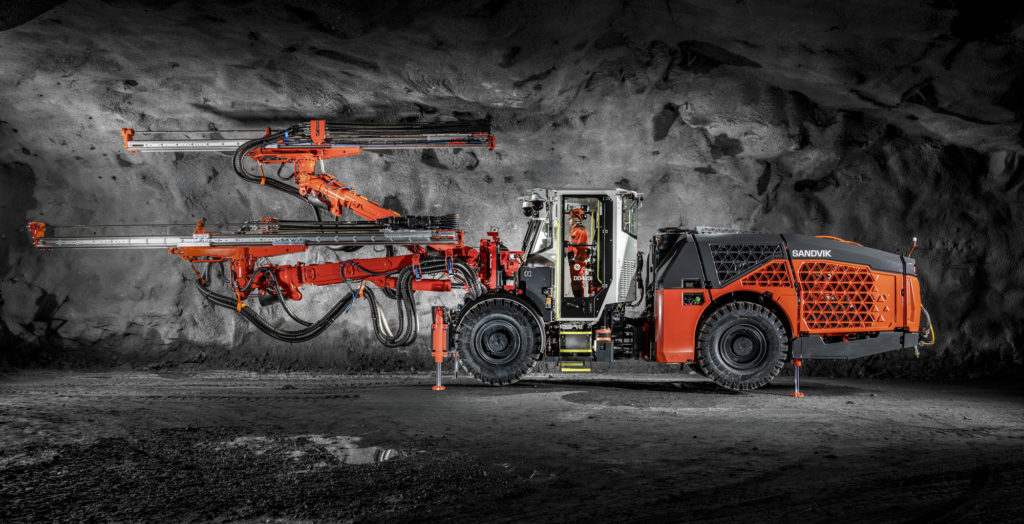
Sandvik has attained IEC 62443-4-1 Maturity Level 3 (ML3) certification for its secure product development lifecycle, marking a significant advancement from its previous Maturity Level 2 (ML2) achieved in 2025. This certification confirms that Sandvik systematically embeds cybersecurity practices in the development and maintenance of its mining technologies. The assessment was supported by evidence from Sandvik Intelligent Control Architecture (SICA), which is utilized across its i-series mining equipment. As mining operations increasingly rely on connected and autonomous technologies, this certification aims to enhance customer confidence in the cybersecurity of these systems. Riku Pulli, President of Digital Mining Technologies at Sandvik, emphasized the importance of integrating security throughout the product lifecycle. The achievement follows Sandvik Mining's ISO/IEC 27001 certification, reinforcing its commitment to cybersecurity in the mining sector.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Cisco FMC Vulnerabilities Under Active Exploitation Cisco's Secure Firewall Management Center (FMC) Software has two critical vulnerabilities, CVE-2026-20079 and CVE-2026-20316, that are currently being exploited by state-sponsored and ransomware actors. CVE-2026-20079, rated 10.0 on the CVSS scale, allows unauthenticated remote attackers to bypass authentication and… Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…