 Payloadspace
Satlyt Secures $8M to Enhance AI Capabilities on Satellites
Article Content

- •Satlyt raised $8M to expand its virtual ODC network for AI processing on satellites.
- •The company aims to reduce expensive data downlinking by processing data in orbit.
- •Satlyt plans to onboard 30% of non-Starlink satellites by 2030.
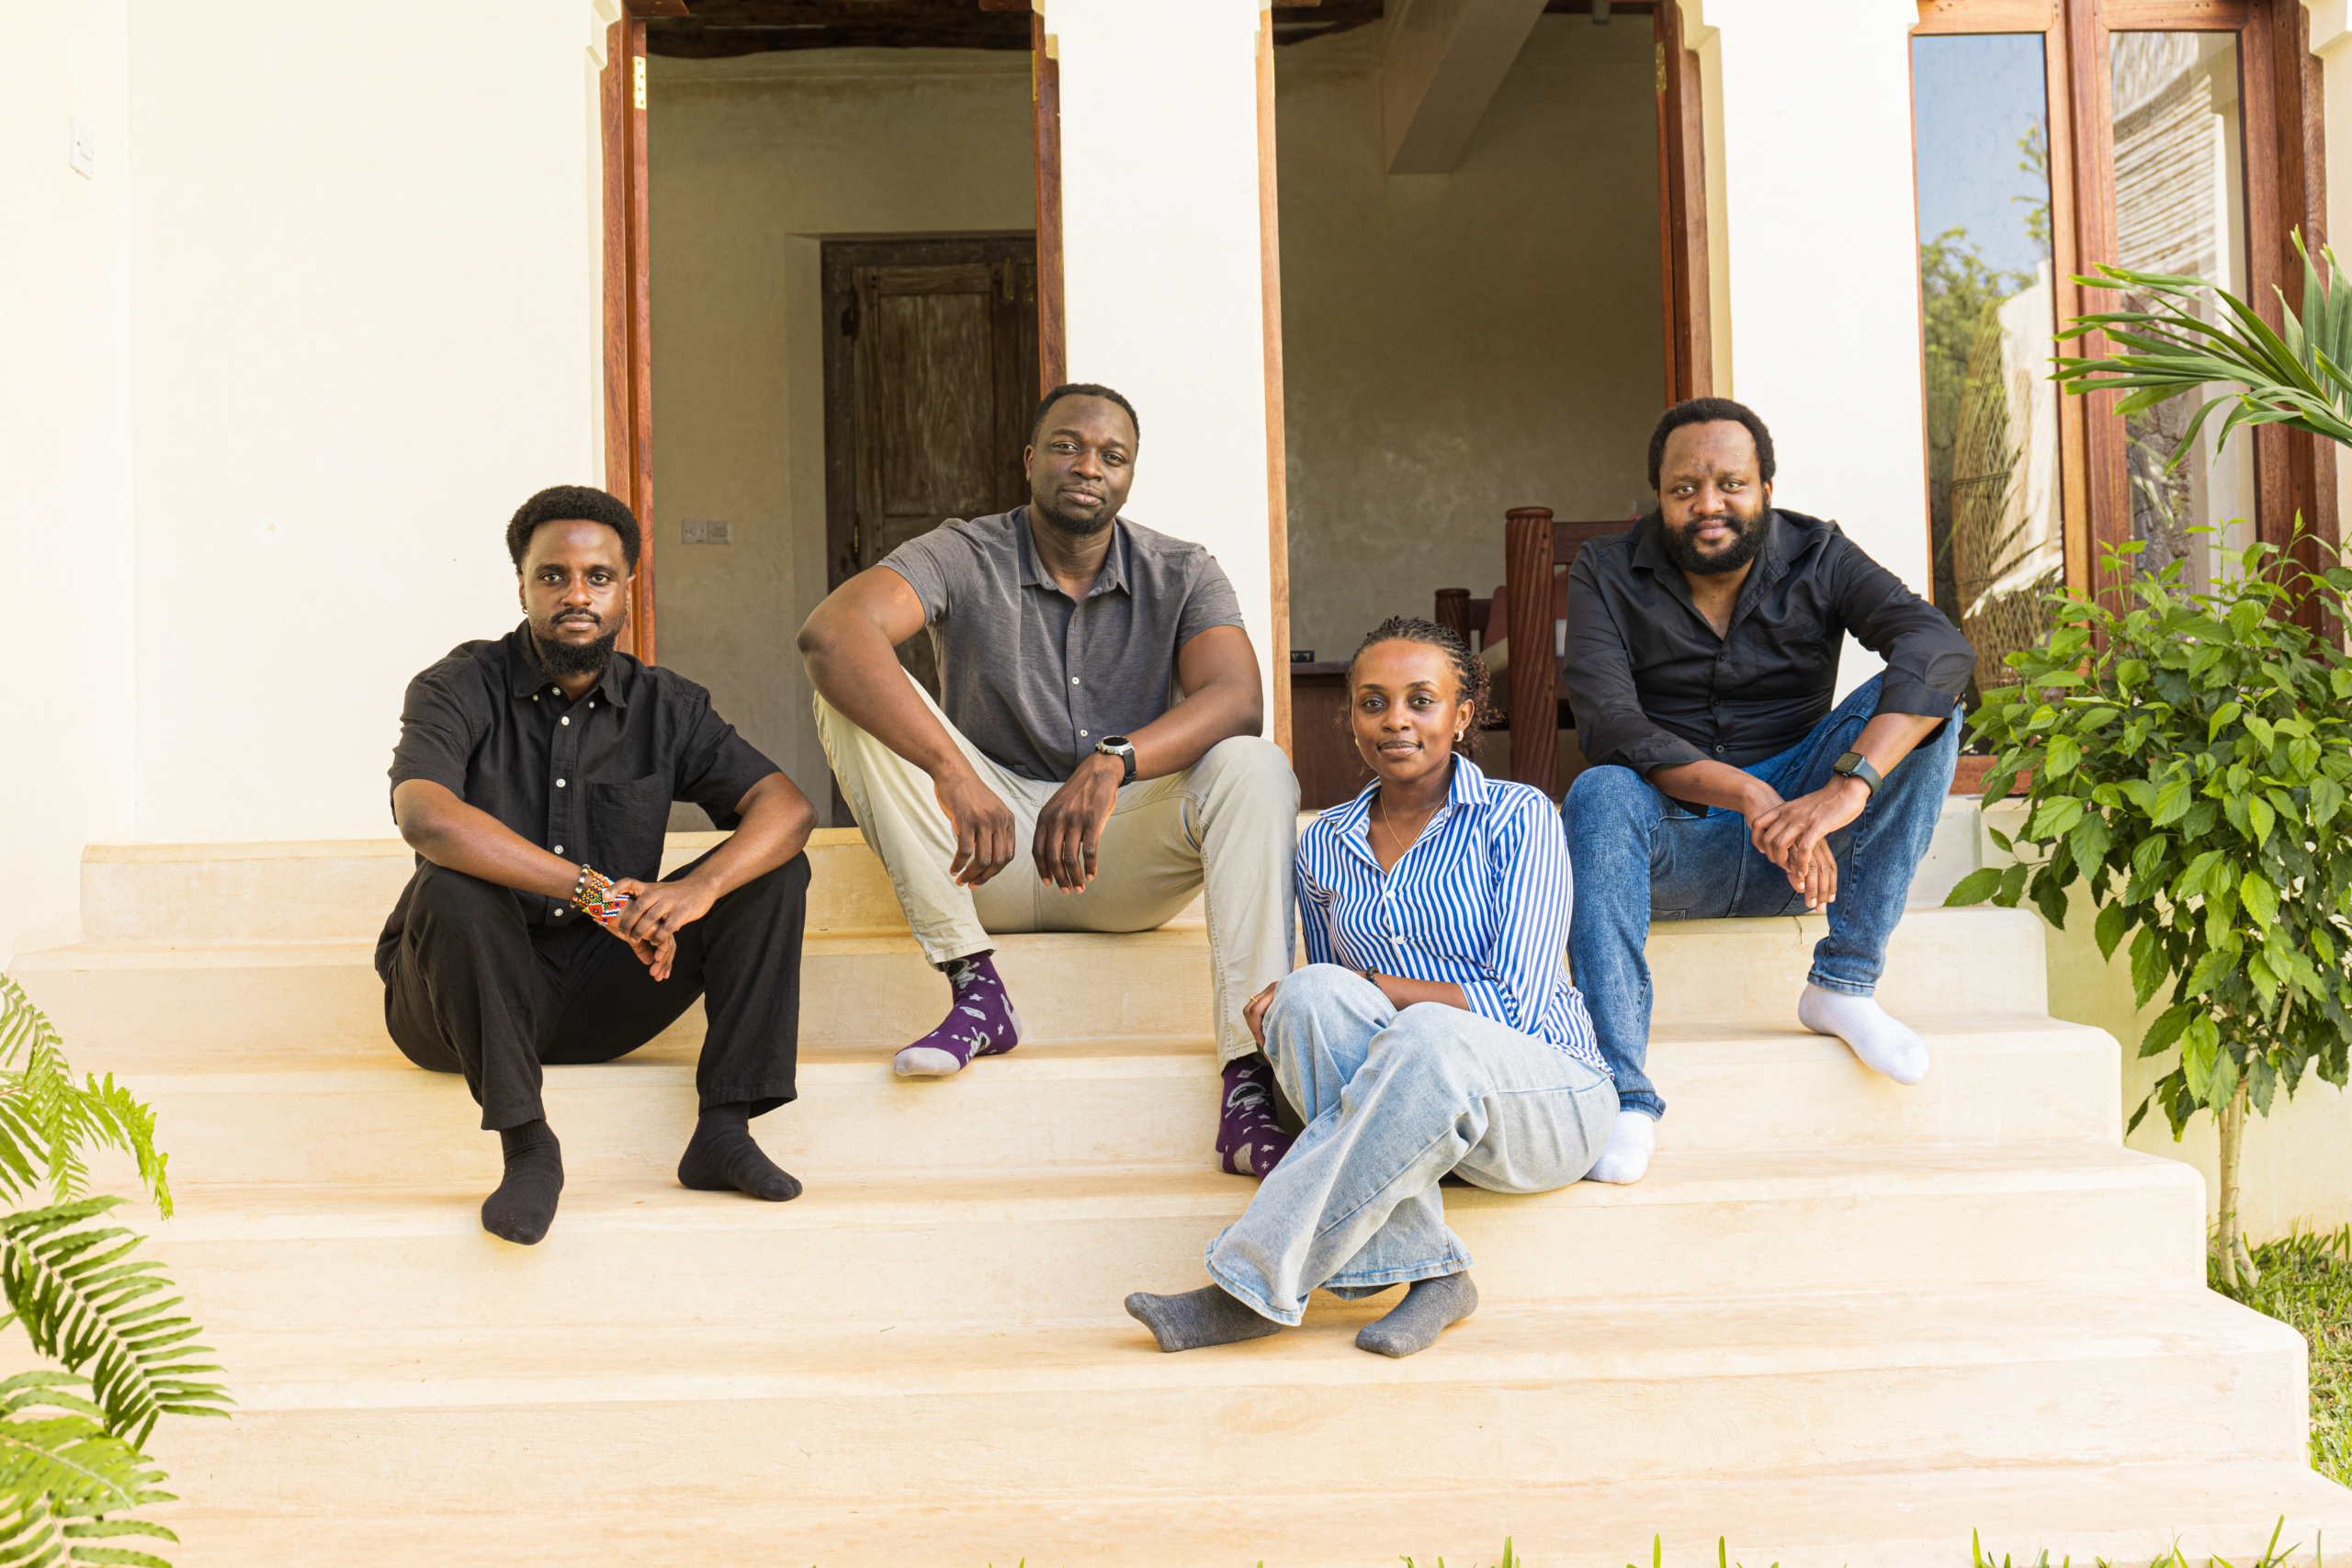
Satlyt, a startup co-founded by former Google and SpaceX engineer Rama Afullo, has raised $8 million in seed funding to expand its virtual orbital data center (ODC) network. The company aims to deploy AI capabilities on satellites to process data in orbit, reducing the need for expensive downlinking to Earth. Satlyt's software has already been tested successfully on two demonstration missions, including a significant collaboration with NASA. The funding round was led by non sibi ventures and aims to enhance Satlyt's team and in-orbit capabilities. The startup plans to onboard 30% of non-Starlink satellites by the end of the decade, positioning itself as a complementary solution to hardware-focused ODC concepts. The company's approach contrasts with traditional satellite operations by focusing on software rather than spacecraft construction.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Common questions
What is Satlyt's main goal?
Who led the funding round?
What are Satlyt's future plans?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…