 Aa.Tr
Saudi Coalition Intercepts Houthi Drone in Riyadh Amid Escalating Tensions
Article Content

- •Saudi-led coalition intercepted a drone in Riyadh on October 22, 2026.
- •The drone's origin and intended target remain undisclosed.
- •The incident is part of escalating hostilities between the Saudi coalition and Houthi forces.
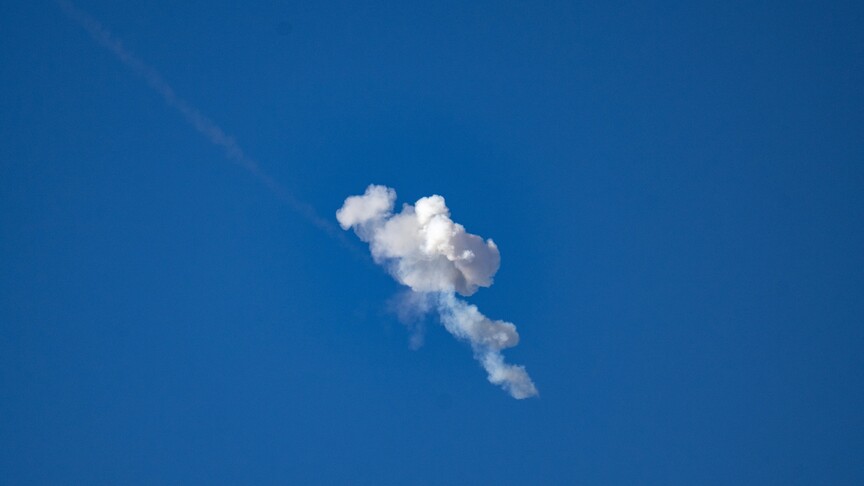
On October 22, 2026, the Saudi-led coalition announced the interception and destruction of a drone in the Riyadh region. Coalition spokesperson Turki al-Maliki confirmed the incident via a statement on social media, but did not disclose the drone's origin or intended target. This event occurs against a backdrop of increasing hostilities between the Saudi coalition and Yemen's Houthi group, which has been targeting Saudi airports and energy facilities. The Houthi group has previously claimed responsibility for drone attacks against Saudi Arabia, indicating a potential escalation in the conflict. The situation remains tense, with ongoing military engagements reported in the region.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track QatarEnergy in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What was the drone's origin?
What are the implications of this incident?
Has there been a response from the Houthi group?
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Lazarus APT Launches Operation FlashHole Using AI and Post-Quantum Cryptography Kaspersky has identified a cyberespionage campaign, dubbed Operation FlashHole, attributed to the Lazarus APT group, active since July 2025. The campaign has targeted at least three organizations in South Korea's construction, software, and wire-communication sectors. Attack methods include spear-phishing emails…