 Latimes
Scottish Police Investigate Ex-Prince Andrew's Links to Epstein at Balmoral
Article Content

- •Scottish police are investigating former Prince Andrew's ties to Epstein at Balmoral.
- •New allegations suggest women may have been trafficked to the royal estate.
- •Andrew was previously arrested in February 2026 for misconduct related to Epstein.
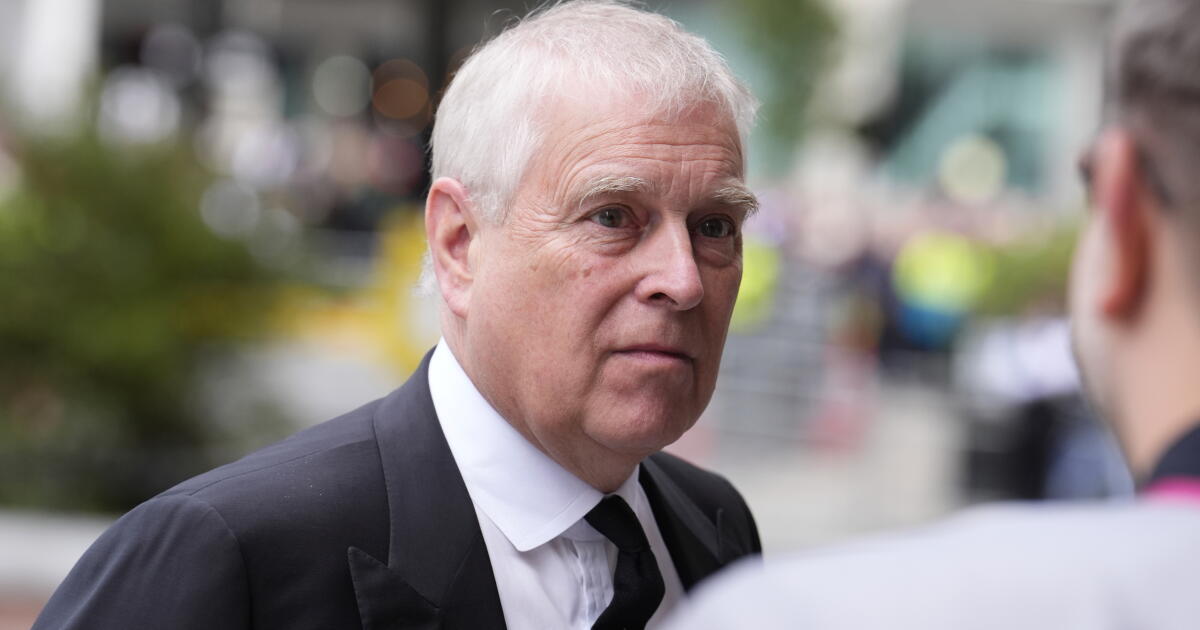
Scottish police have launched an investigation into former Prince Andrew's interactions with Jeffrey Epstein and Ghislaine Maxwell at Balmoral estate, following new information suggesting women may have been trafficked there. The inquiry is in its early stages, with police stating that all investigations are evidence-led and focused on victim survivors. Images from 1999 showing Epstein and Maxwell at Balmoral were released by the U.S. Department of Justice as part of a broader investigation into Epstein's connections with influential figures. Andrew, who has denied any wrongdoing, was previously arrested in February 2026 on suspicion of misconduct in public office related to Epstein's case. The royal family's reputation has been significantly impacted by Andrew's associations with Epstein, leading to the loss of his royal titles and residence.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What is the basis for the investigation?
What has been Andrew's response to the allegations?
What are the implications for the royal family?
Continue Reading
 North Korean Hackers Steal $6.3 Billion from Binance in Record Crypto Heist On October 29, 2026, Binance, the world's largest cryptocurrency exchange, reported a massive security breach resulting in the theft of approximately $6.3 billion across ten blockchains. The attack is attributed to North Korea's TraderTraitor hacking group, which gained access via a compromised DevOps engineer's…
 Chinese Actor Compromises US Government Networks via PHP2Shell Exploit A suspected Chinese nation-state actor exploited vulnerabilities in Palo Alto Networks firewalls using a chained PHP2Shell exploit and a Linux kernel privilege escalation flaw. The attack, which began on October 23, targeted 25 servers across the US, Japan, Taiwan, and South Korea, with a focus on US…