Critical Vulnerability in syracom AG 2FA Plugin for Atlassian Products
Article Content

- •A broken access control vulnerability in the 2FA plugin allows MFA bypass.
- •Attackers can exploit the flaw using valid user credentials and specific user agents.
- •A patch has been released, and immediate application is recommended.
The Secure Login (2FA) plugin for Atlassian Jira, Confluence, and Bitbucket has a serious broken access control vulnerability. This flaw allows attackers with valid user credentials to bypass multi-factor authentication (MFA) by manipulating the user agent in HTTP requests. Successful exploitation can lead to unauthorized access to administrative settings and the ability to disable the 2FA feature entirely. The vulnerability is particularly dangerous as it affects all user roles, not just administrators. Affected systems include Confluence instances using the syracom AG plugin. The vendor has released a patch that should be applied immediately to mitigate the risk. Security professionals are advised to conduct a thorough review of the product for additional vulnerabilities. The vulnerability underscores the importance of robust security measures in software plugins.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Continue Reading
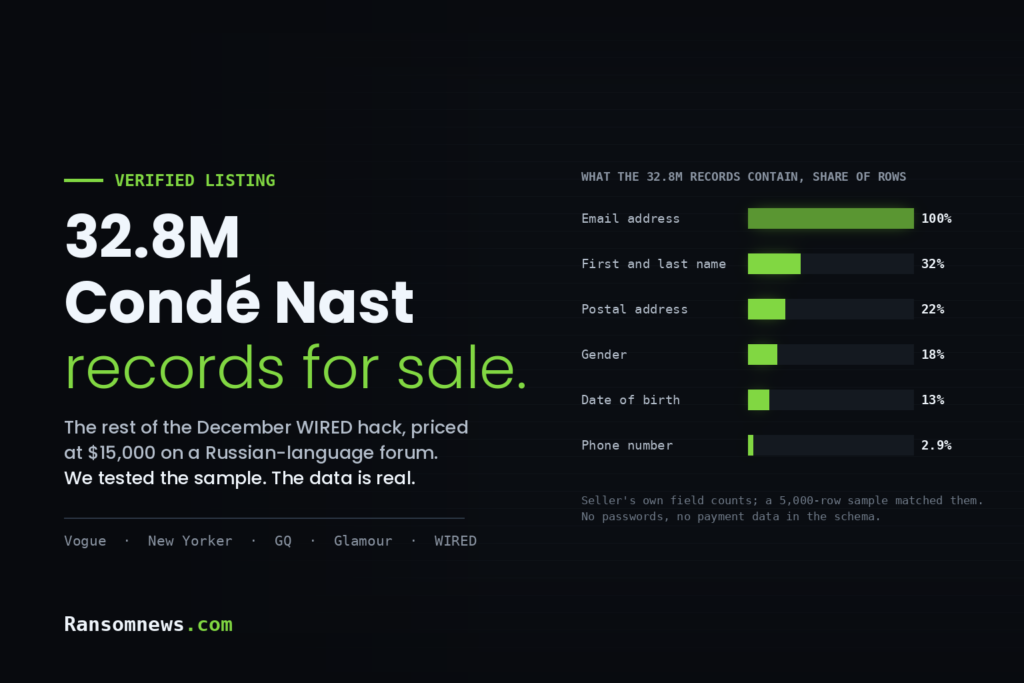 Condé Nast User Data Breach: 32.8 Million Records for Sale On September 7, 2026, a database containing 32,815,767 user records from Condé Nast was listed for sale on a Russian-language hacker forum for $15,000. The data, reportedly collected between September and October 2025, includes unique email addresses, names, postal addresses, gender, birthdays, and phone numbers, but…
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…