 Asiae.Co.Kr
Self-Taught Hacker Leads AI-Powered Data Theft of 8.2 Million Records
Article Content

- •Seven suspects arrested for hacking 90 organizations using generative AI.
- •8.2 million records stolen, including personal and corporate data.
- •Ringleader had no formal IT training, learned hacking through online resources.
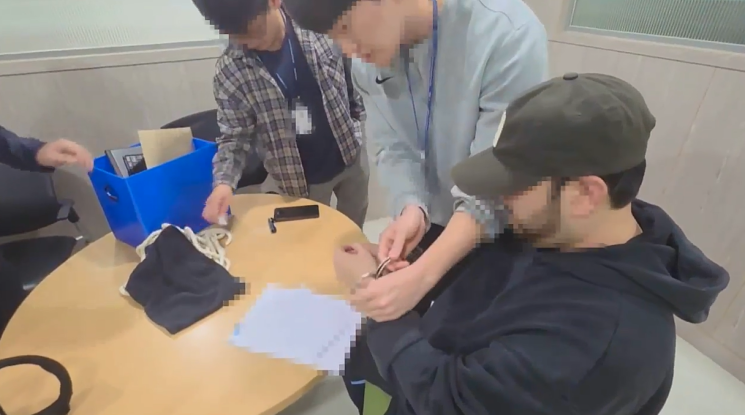
A group of seven individuals, including a self-taught hacker, has been arrested for using generative AI to breach 90 organizations in South Korea, stealing 8.2 million pieces of personal and internal data. The ringleader, who has no formal IT background, reportedly learned hacking techniques online and began using AI tools extensively in August 2026. The group extorted a total of KRW 360 million ($272,000) from the victims, threatening to leak stolen data if payments were not made. The investigation was initiated in June 2026 after a complaint from one of the affected organizations. Police have referred the ringleader to prosecutors while continuing to investigate the other suspects. The victims included hospitals, private academies, and subsidiaries of major corporations.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Common questions
What types of organizations were targeted?
What was the total amount demanded from victims?
How did the ringleader learn hacking?
Continue Reading
 .NET Vulnerability CVE-2026-111497 Requires Immediate Action On October 25, 2026, Microsoft released out-of-band security updates for.NET addressing CVE-2026-111497, a vulnerability in the Brotli decompression algorithm that allows unauthorized attackers to elevate privileges over a network. The flaw affects.NET versions 8, 9, 10, and 11, particularly in applications that…
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…