 Philstar
Senate Leadership Dispute Heightens Security Amid Payroll Concerns
Article Content

- •Gatchalian assured Senate employees their pay is secure amid leadership disputes.
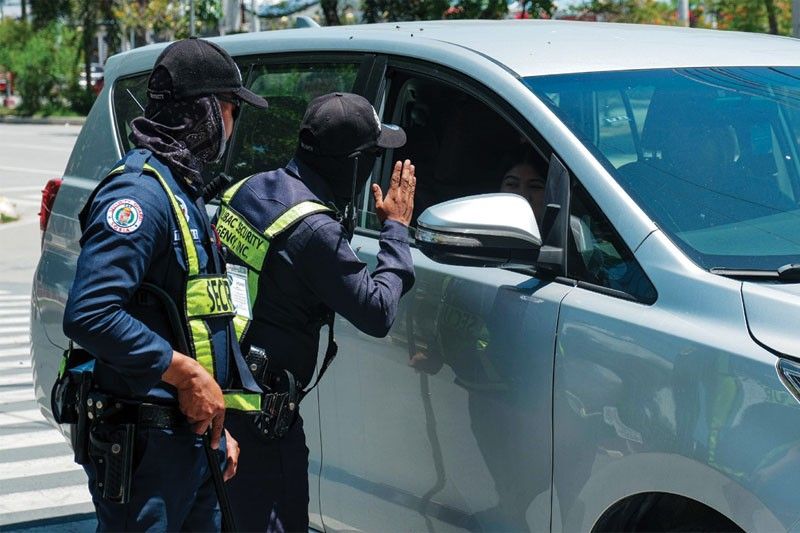
- •Heightened security measures were implemented due to a threat linked to a fugitive.
- •Cayetano's proposals for shared administrative duties were rejected by Gatchalian.
Amid a leadership dispute in the Philippine Senate, Acting Senate President Sherwin Gatchalian reassured over 2,000 employees that their salaries and benefits would not be affected. Gatchalian held a Zoom press briefing to address employee concerns and announced heightened security measures due to a security threat linked to former associates of a fugitive. He emphasized that operational expenses would continue despite the political bickering, as he worked on payroll arrangements and employee promotions. Gatchalian dismissed proposals from Senator Alan Peter Cayetano, who insisted on sharing administrative duties. The Senate has implemented a work-from-home setup due to the security threat, which has led to compliance from employees. Gatchalian's authority as the acting Senate President was reiterated, while Cayetano's advisories were largely ignored by the staff. The situation remains tense as the Senate prepares for an upcoming impeachment trial.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…