 Gpsworld
Septentrio Launches Advanced GNSS Module with Anti-Jamming Features
Article Content
Browse articles 
- •The mosaic-G5 P6 module offers advanced anti-jamming and spoofing protection.
- •It supports high-accuracy positioning and is compatible with major open-source autopilots.
- •An evaluation kit is available for easy integration into various systems.
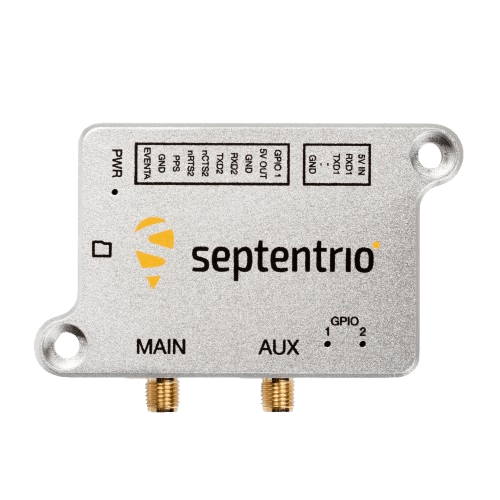
Septentrio has introduced the mosaic-G5 P6 multi-frequency GNSS module, designed for precise positioning in UAVs and robotics. This compact module, measuring 23 mm by 16 mm and weighing 2.2 grams, includes AIM+ Premium technology to protect against GNSS jamming and spoofing. It offers high update rates and low latency, crucial for industrial applications. The module supports Galileo High Accuracy Service for decimeter-level positioning and is compatible with popular open-source autopilots. An evaluation kit is also available, enabling easy integration and testing. The launch coincides with the Xponential event in Detroit, where the product is showcased.
Ask AI about this cluster
Answers cite the sources they use
Updated 132d ago How this analysis works
Timeline
2026-05-11
Launch of mosaic-G5 P6 GNSS module
Septentrio introduced the mosaic-G5 P6, featuring anti-jamming technology and high precision for UAVs and robotics.
Gpsworld2026-05-11
Evaluation kit for mosaic-G5 P6 released
The mosaic-go G5 P6 evaluation kit was launched, designed for easy testing and integration of the GNSS module.
shop.septentrio.comMore articles in this cluster (4)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…