 Scworld
ShadowHS Malware Framework Targets Linux Systems with Fileless Techniques
Article Content
Browse articles 
The ShadowHS malware framework has been identified as a significant threat to Linux environments, utilizing a fileless architecture for stealthy operations. Discovered by Cyble Research & Intelligence Labs on January 30, 2026, ShadowHS employs a multi-stage encrypted loader for in-memory execution, enabling attackers to perform credential theft, privilege escalation, and data exfiltration without leaving persistent files on the system.
Ask AI about this cluster
Answers cite the sources they use
Updated 228d ago How this analysis works
More articles in this cluster (4)
Following this threat?
Track Ebury in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
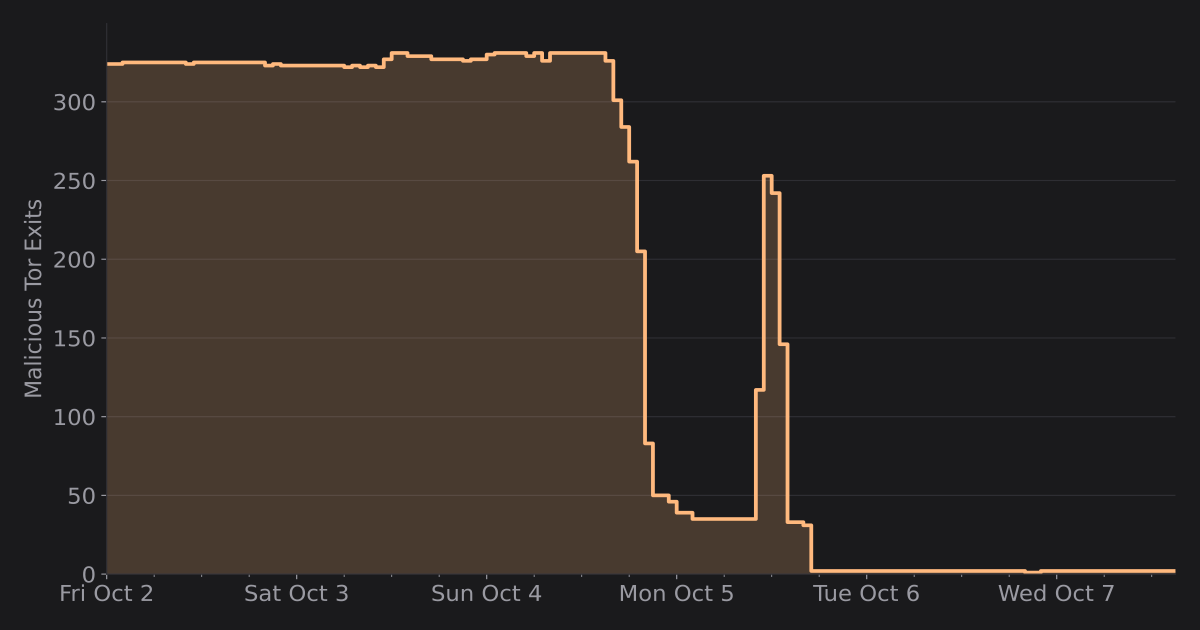 Over 300 Tor Exit Nodes Compromised in SSH Interception Attack On October 2, 2026, 333 infected Tor exit nodes began a coordinated campaign to intercept SSH connections and collect unencrypted data. The attackers had gained access to these nodes two months prior, deploying the Ebury 1.8.3 payload, which is an OpenSSH backdoor and credential stealer for Linux. The attack…
 .NET Vulnerability CVE-2026-111497 Requires Immediate Action On October 25, 2026, Microsoft released out-of-band security updates for.NET addressing CVE-2026-111497, a vulnerability in the Brotli decompression algorithm that allows unauthorized attackers to elevate privileges over a network. The flaw affects.NET versions 8, 9, 10, and 11, particularly in applications that…