 English.Elpais
Sheinbaum Rejects Foreign Interference Amid U.S. Pressure
Article Content

- •Sheinbaum's speech emphasized Mexico's sovereignty against U.S. pressures.
- •Recent constitutional reforms limit foreign intervention and impose penalties on violators.
- •The speech was delivered before the 2027 midterm elections, highlighting domestic and external challenges.
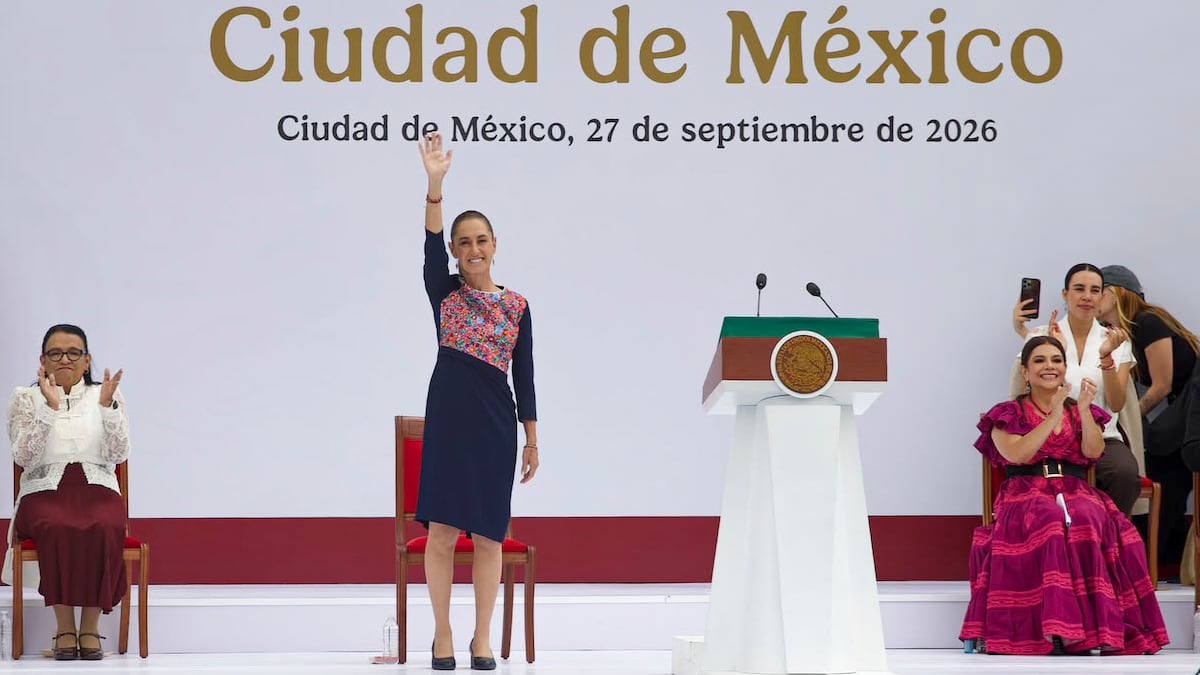
On September 28, 2026, President Claudia Sheinbaum delivered a speech at Mexico City's Zócalo, strongly rejecting foreign interference, particularly from the United States, amid ongoing tensions over drug trafficking. She emphasized that decisions regarding Mexico's future should be made solely by its people, linking this stance to historical struggles for independence. The speech coincided with rising U.S. pressures, including offers to send troops to Mexico and allegations against Mexican politicians regarding ties to criminal organizations. Sheinbaum highlighted recent constitutional reforms aimed at limiting foreign intervention and imposing penalties on foreign agents involved in illicit activities. These reforms were introduced after the U.S. designated organized crime groups as terrorist organizations, which Sheinbaum argues should not justify foreign intervention. The president's remarks come as she approaches her third year in office and prepares for the 2027 midterm elections, amidst a backdrop of internal party struggles and external geopolitical challenges.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Zero-Day Vulnerability in F5 BIG-IP APM Exploited for Remote Code Execution F5 Networks has reported a critical vulnerability in its BIG-IP Access Policy Manager (APM), tracked as CVE-2026-94127, which is being actively exploited in the wild. The flaw allows unauthenticated attackers to execute remote code on systems configured with both an APM access policy and an OAuth profile. This…