 Securityaffairs
ShinyHunters Suspect Arrested in Jordan Assists FBI Investigation
Article Content

- •Saif al-Din Khader arrested in Jordan is cooperating with the FBI.
- •ShinyHunters claims to have stolen sensitive data on every FBI employee.
- •The FBI is actively investigating the group and has made multiple arrests.
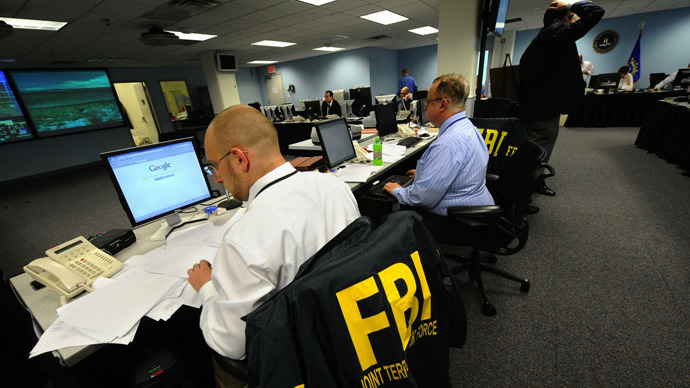
Saif al-Din Khader, a suspected member of the ShinyHunters hacking group, was arrested in Jordan and is reportedly cooperating with the FBI to track down the group. The ShinyHunters claim to have stolen sensitive data on every FBI employee, including personal and medical records. Khader is providing investigators with access to his devices and communications to help identify other members of the group. The FBI has stated it is aggressively investigating the cyber incident involving ShinyHunters and has already arrested multiple individuals linked to the group. A separate arrest of a Dutch hacker, Pepijn van der Stap, was also confirmed, linking him to ShinyHunters through his online alias 'Umbreon'. The implications of these arrests could be significant, especially if the claims about the stolen data are validated, drawing comparisons to the 2015 OPM breach.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Scattered Spider and FBI in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What data did ShinyHunters claim to steal?
What is the current status of the investigation?
How is Khader assisting the FBI?
Continue Reading
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…