 shuftipro.com
Shufti Recognized as Leading KYC Vendor in 2026 Liminal Index
Article Content

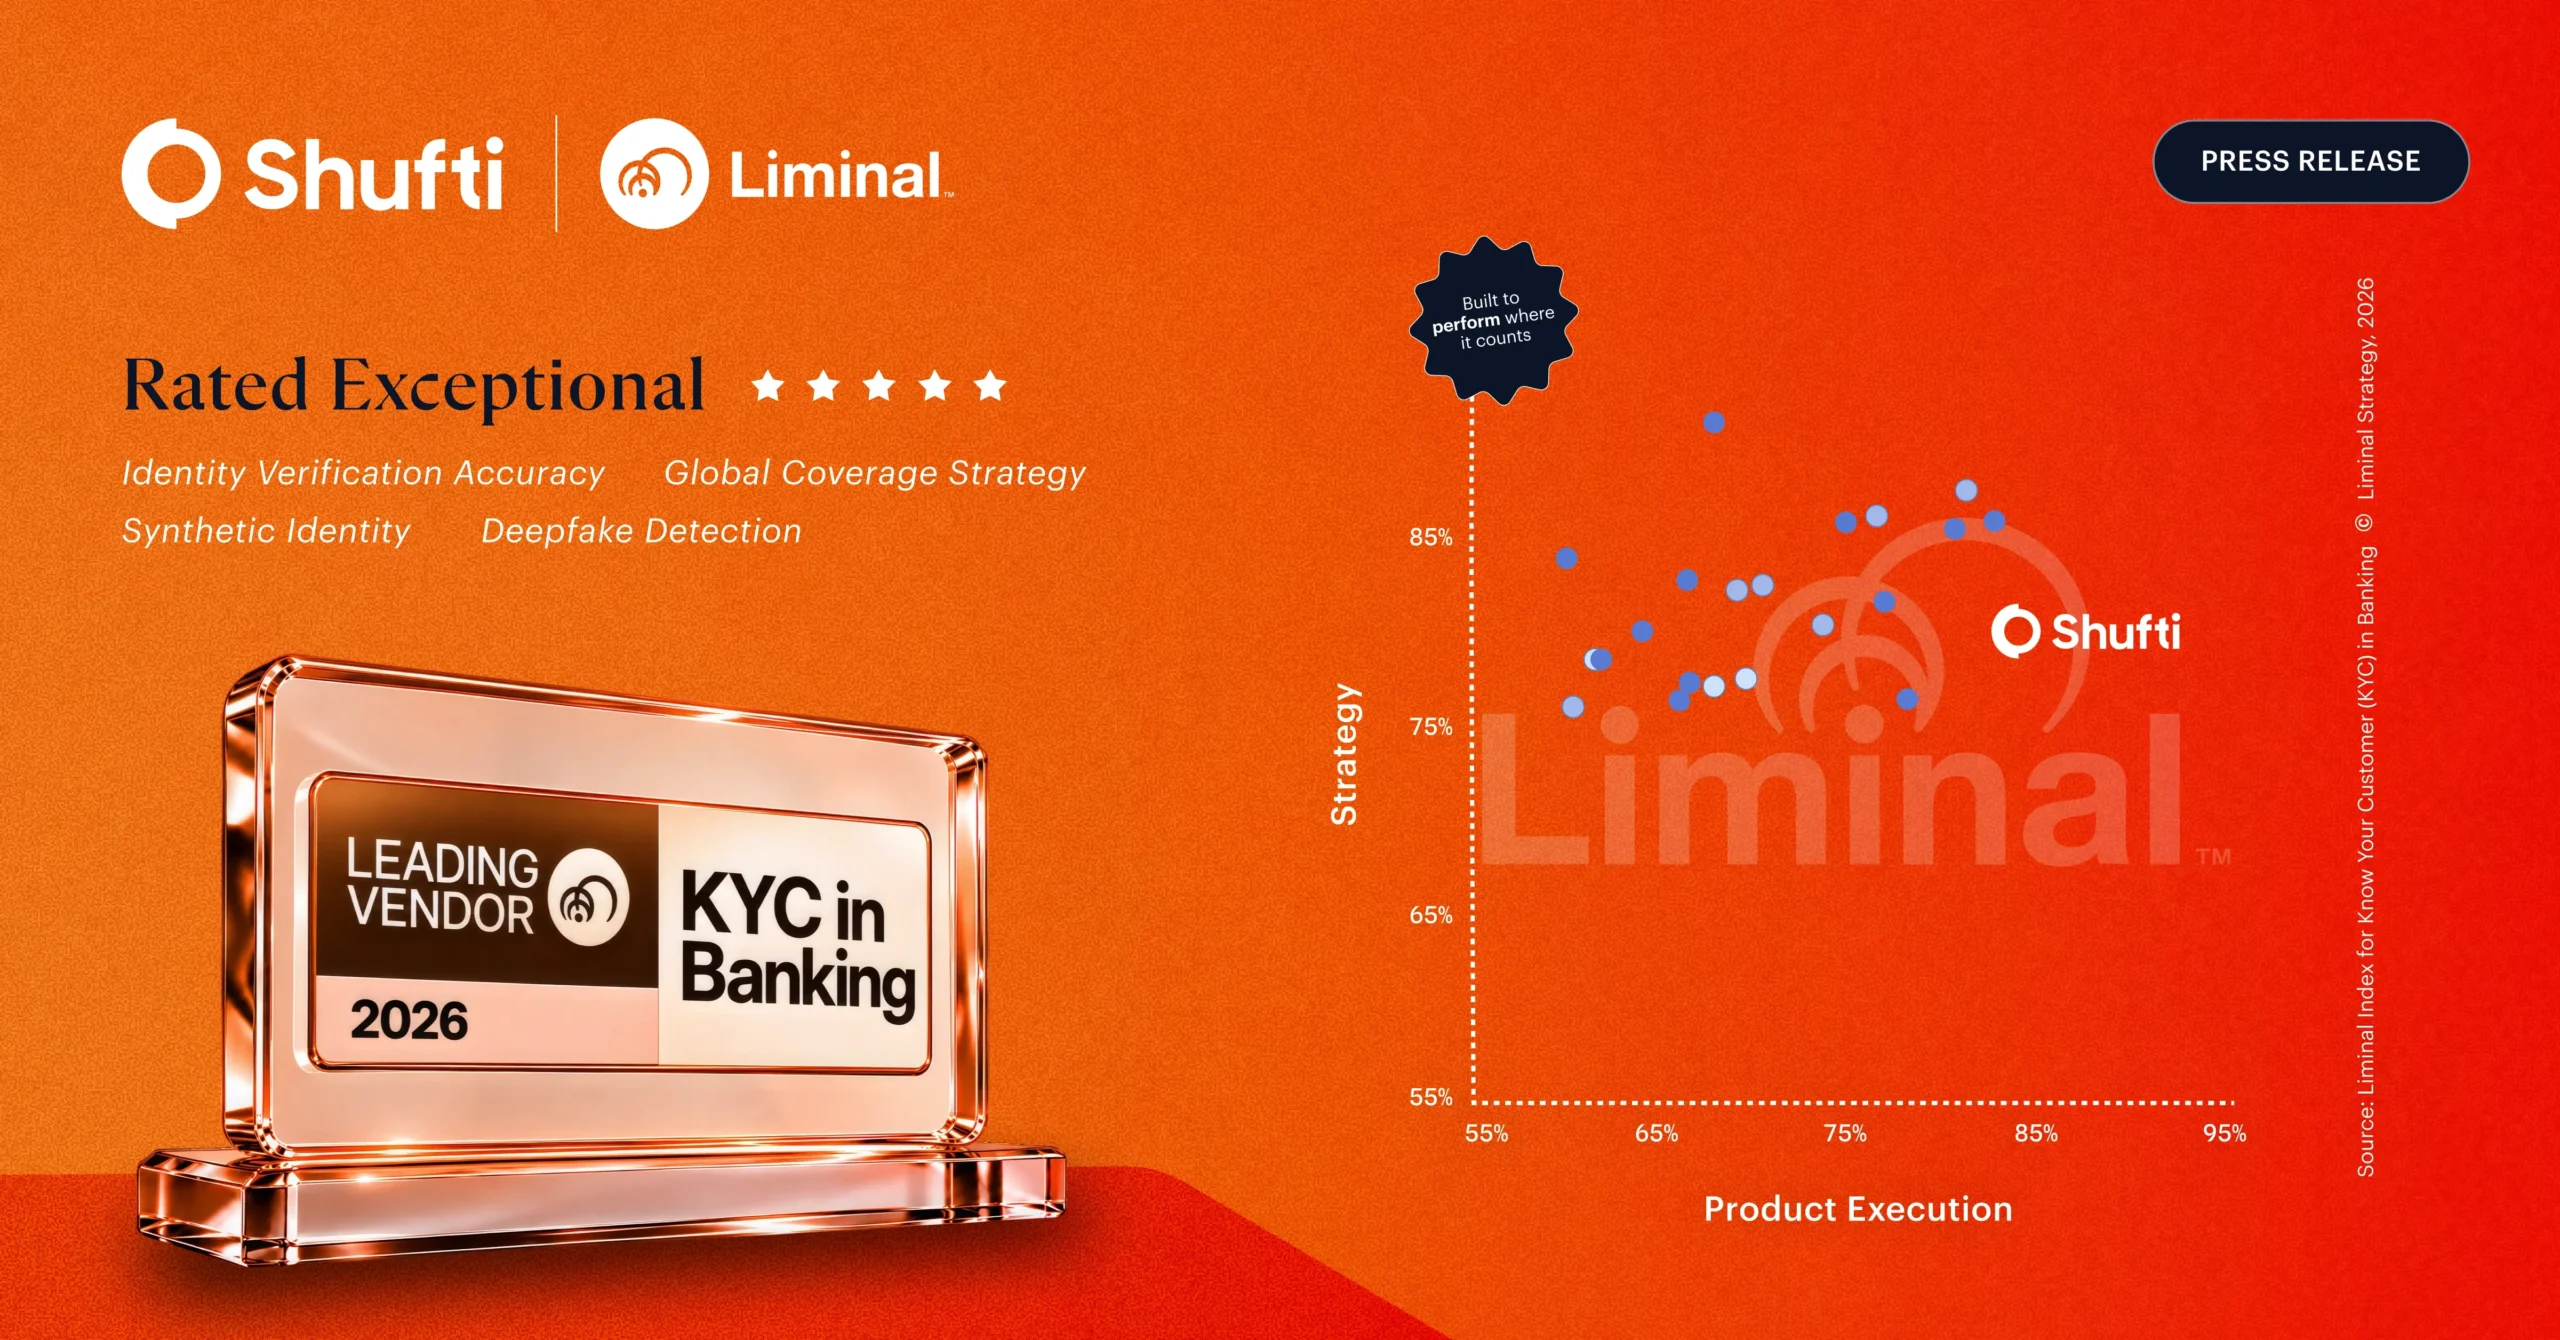
- •Shufti scored 83% in Product Execution, the highest in the Liminal Index.
- •The Liminal Index evaluated 82 vendors, identifying 22 as leading vendors.
- •98.8% of banks plan to implement perpetual KYC in the next 12 months.
Shufti has been named a Leading Vendor in the 2026 Liminal Index™ for Know Your Customer (KYC) in Banking, achieving the highest score of 83% in Product Execution. The Liminal Index evaluated 82 vendors and identified 22 leading vendors, with Shufti receiving Exceptional ratings in six criteria, including Identity Verification Accuracy and Deepfake Detection. The report highlights a shift in KYC expectations due to upcoming regulations, with 98.8% of banks planning to deploy perpetual KYC within the next year. Shufti's global coverage strategy and automation capabilities were noted as key differentiators. The findings are based on a survey of 100 banking KYC decision-makers conducted in March 2026.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What criteria did Shufti excel in?
How many vendors were evaluated in the Liminal Index?
What is the significance of the Liminal Index report?
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Lazarus APT Launches Operation FlashHole Using AI and Post-Quantum Cryptography Kaspersky has identified a cyberespionage campaign, dubbed Operation FlashHole, attributed to the Lazarus APT group, active since July 2025. The campaign has targeted at least three organizations in South Korea's construction, software, and wire-communication sectors. Attack methods include spear-phishing emails…