 Straitstimes
Singapore Police Investigate $4.4M Scam Linked to Phishing Ads
Article Content

- •280 individuals are under investigation for scams totaling nearly $4.4 million.
- •Phishing scams exploited fraudulent social media ads targeting bargain shoppers.
- •Victims reported losses of $410.6 million in the first half of 2026.
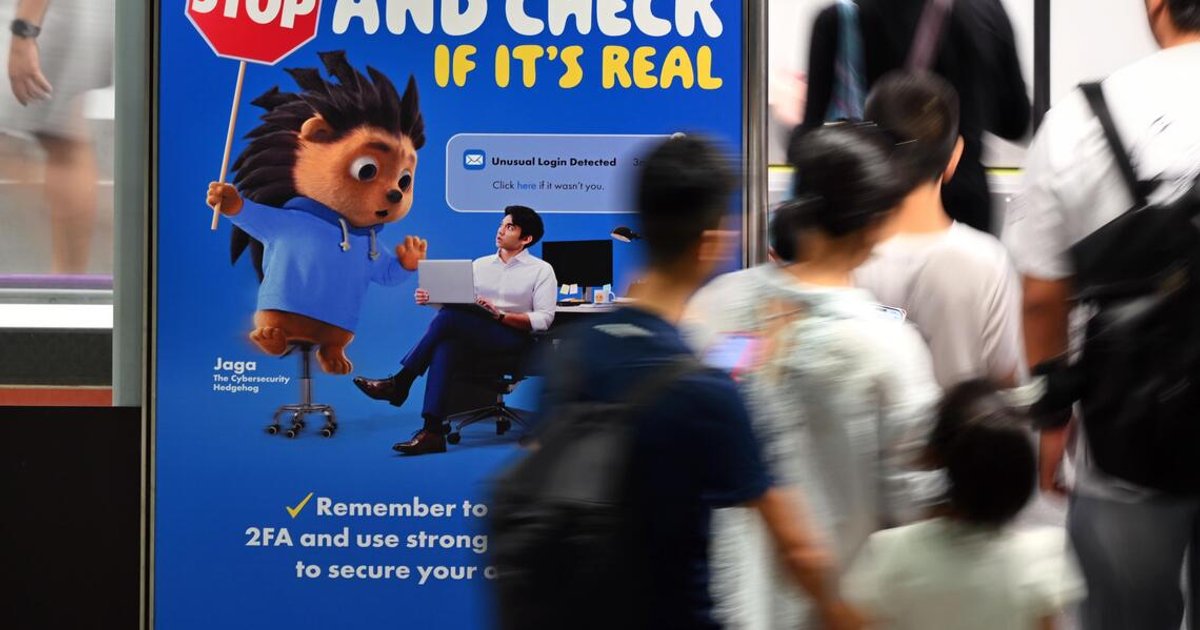
Singapore police are investigating 280 individuals, aged 15 to 81, in connection with scams resulting in nearly $4.4 million in losses. The suspects are linked to over 633 cases, including phishing scams that exploited fraudulent social media ads. Victims were lured by ads for low-cost products, leading them to phishing websites that collected sensitive banking information. In the first half of 2026, scam victims in Singapore reported losses of $410.6 million, with a notable increase in phishing-related incidents. Police have urged the public to enhance account security and recognize warning signs of scams. The investigation followed a two-week operation conducted from September 24 to October 7, 2026. Those found guilty may face severe penalties, including imprisonment and caning. The police continue to recover funds from scam victims, totaling over $97 million this year.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What types of scams are being investigated?
How much money was lost to scams in Singapore this year?
What penalties do suspects face if convicted?
Continue Reading
 Critical Authentication Bypass in Rejetto HFS Exploited Within 24 Hours Anthropic's Mythos model identified a critical authentication bypass in Rejetto HTTP File Server (HFS), tracked as CVE-2026-61500, allowing remote code execution. Discovered by Horizon3 researcher Zach Hanley, the flaw was revealed on September 27, 2026, and exploitation began within 24 hours, with attacks traced to…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on…