 Abc7Ny
Single Mother Victimized by Child Support Debit Card Scam
Article Content
Browse articles 
- •A single mother lost $3,495.72 due to a debit card scam.
- •The scam involved unauthorized cash-back transactions at a grocery store.
- •State agency denied fraud claim despite evidence of the mother's innocence.
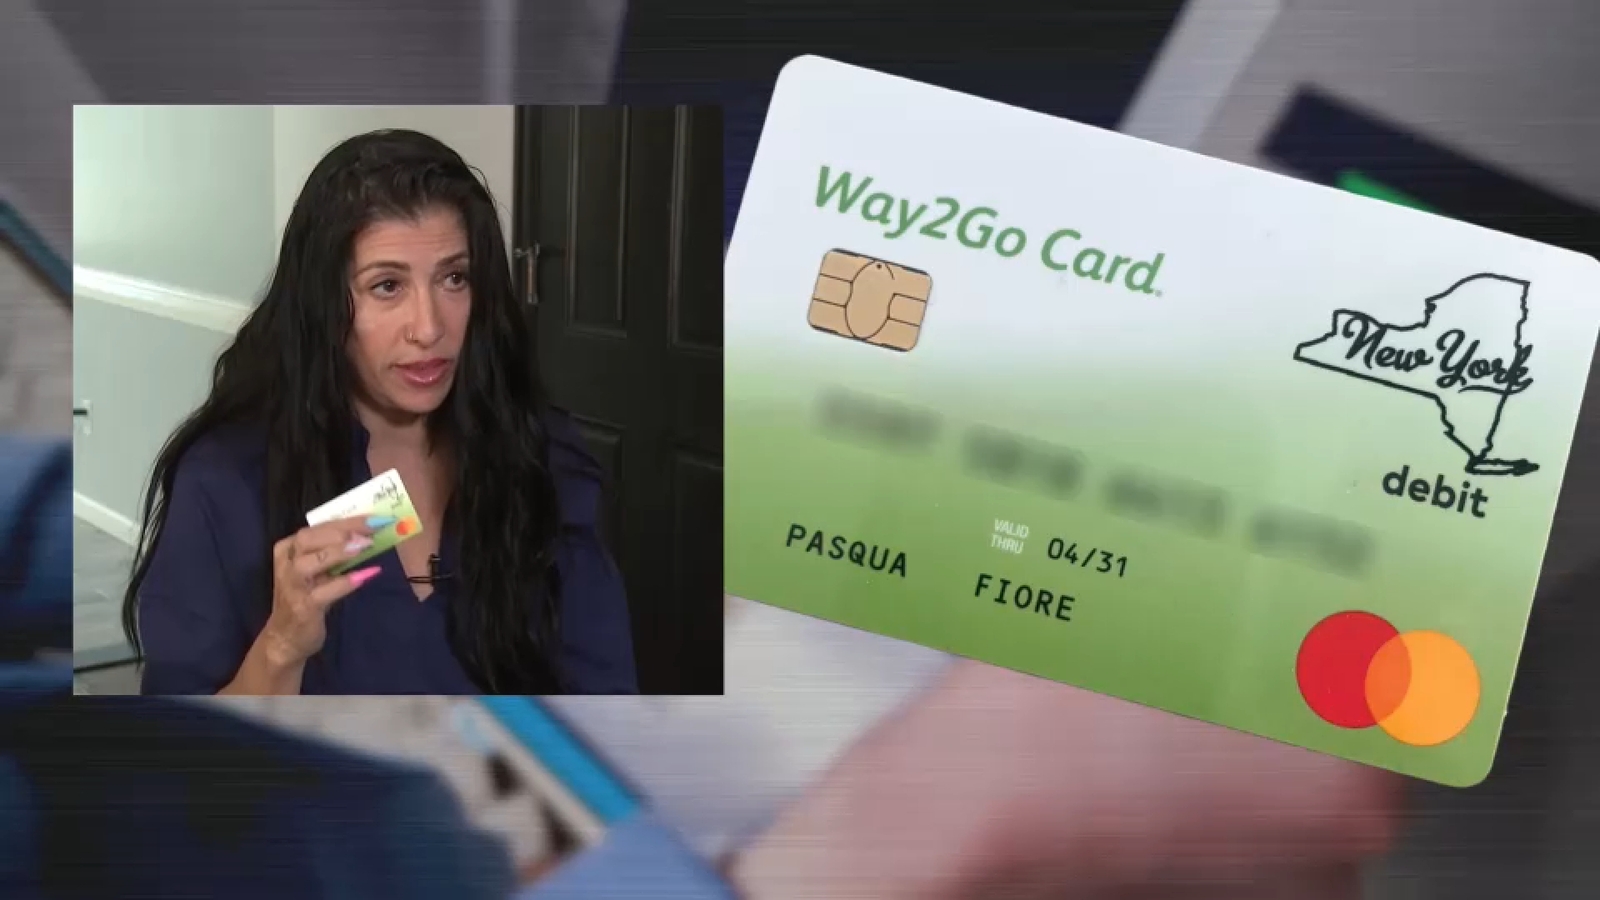
A Goshen mother, Pasqua Fiore, had her child support debit card hacked multiple times, losing $3,495.72. The scam involved unauthorized cash-back transactions made by a suspect at a grocery store in Brooklyn while Fiore was at her bank in Goshen. Despite filing a police report and providing evidence of her whereabouts, the state agency denied her fraud claim, stating 'no error occurred.' Fiore's new card was sent to a different address, complicating her situation further. This incident highlights the vulnerability of social service debit cards to fraud and the challenges victims face in recovering lost funds.
Ask AI about this cluster
Answers cite the sources they use
Updated just now How this analysis works
Timeline
2026-09-16
Mother reports debit card scam
Pasqua Fiore reported her child support debit card was hacked and drained, losing $3,495.72.
Abc7Ny2026-09-16
Police investigation initiated
Goshen Police Chief Ryan Rich confirmed the scam and began investigating the unauthorized transactions.
Abc7Ny2026-09-16
State agency denies fraud claim
The New York Office of Temporary and Disability Assistance wrote that 'no error occurred' in Fiore's case.
Abc7NyMore articles in this cluster (2)
Continue Reading
 Critical Cisco FMC Vulnerabilities Under Active Exploitation Cisco's Secure Firewall Management Center (FMC) Software has two critical vulnerabilities, CVE-2026-20079 and CVE-2026-20316, that are currently being exploited by state-sponsored and ransomware actors. CVE-2026-20079, rated 10.0 on the CVSS scale, allows unauthenticated remote attackers to bypass authentication and… Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…