 News.Online.Ua
Slovak PM Fico Threatens to Block EU Sanctions Over Druzhba Pipeline Dispute
Article Content

- •Slovak PM Fico threatens to block EU sanctions if Ukraine does not reopen the Druzhba pipeline.
- •Fico accuses the EU of double standards, favoring Ukraine over Slovakia's interests.
- •The Druzhba pipeline is vital for oil supplies to Slovakia and Hungary, impacting regional energy security.
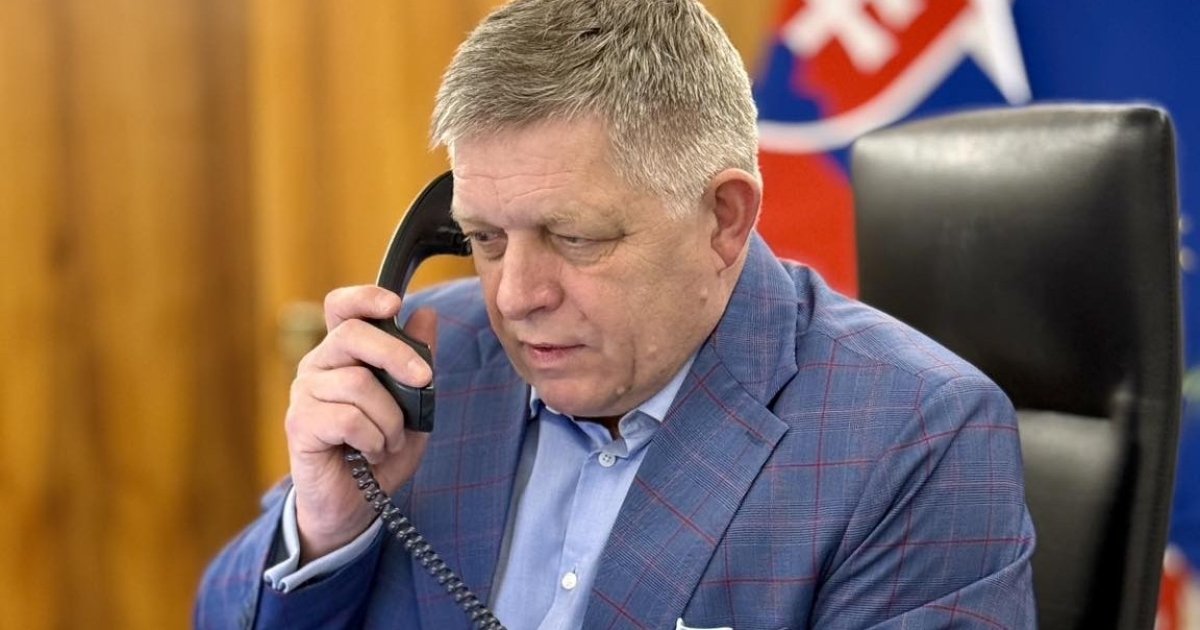
Slovak Prime Minister Robert Fico announced he would veto the EU's 20th sanctions package against Russia if the European Commission does not pressure Ukraine to resume oil transit through the Druzhba pipeline. In a video address, Fico criticized both the European Commission and Ukrainian President Volodymyr Zelenskyy, accusing them of prioritizing Ukraine's interests over those of EU member states. He claimed Slovakia received a threatening letter from Brussels regarding its domestic fuel market protections, while Ukraine received supportive communications. Fico's stance reflects ongoing tensions over the pipeline, which is crucial for oil deliveries to Slovakia and Hungary. He has previously warned that Slovakia would block a significant EU loan to Ukraine if inspections of the damaged pipeline were not permitted. The situation highlights a growing rift within the EU regarding energy security and geopolitical alliances.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (37)
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Lazarus APT Launches Operation FlashHole Using AI and Post-Quantum Cryptography Kaspersky has identified a cyberespionage campaign, dubbed Operation FlashHole, attributed to the Lazarus APT group, active since July 2025. The campaign has targeted at least three organizations in South Korea's construction, software, and wire-communication sectors. Attack methods include spear-phishing emails…