 Securityaffairs.Co
SmartLoader Campaign Uses Fake Oura MCP Server to Distribute StealC Malware
Article Content
Browse articles 
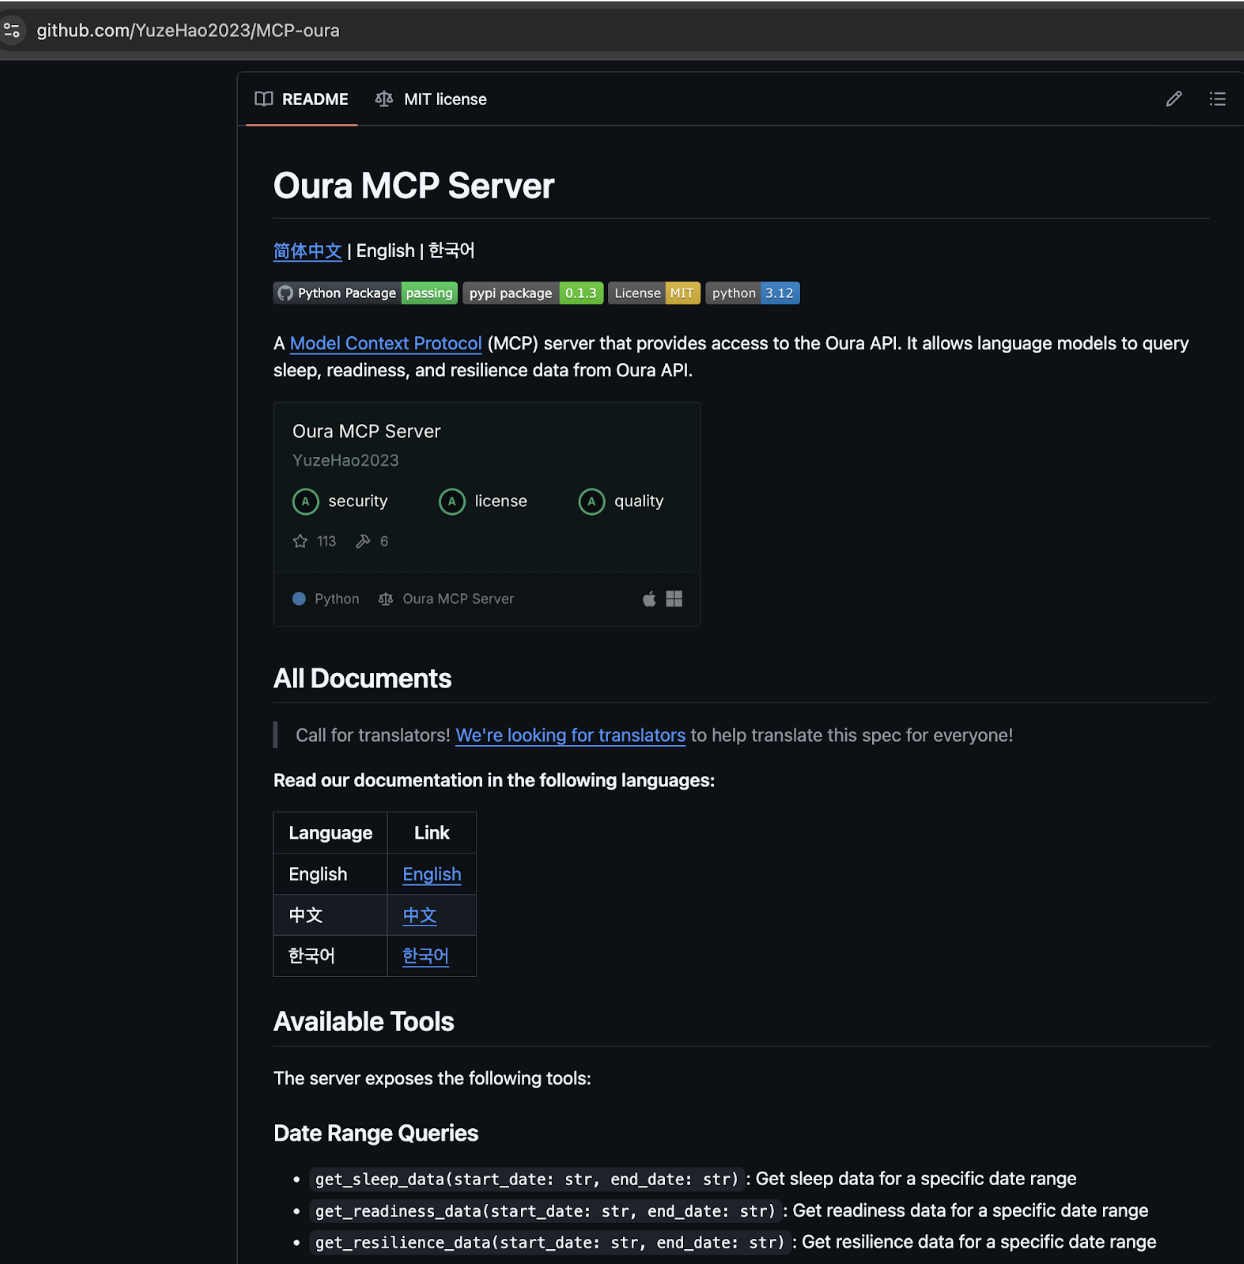
Hackers exploited a cloned Oura MCP server to distribute the StealC info-stealer malware. The attack was uncovered by Straiker’s AI Research (STAR) Labs, revealing that the fake project was designed to appear legitimate, complete with counterfeit forks to deceive users into downloading the malware.
Ask AI about this cluster
Answers cite the sources they use
Updated 211d ago How this analysis works
Timeline
2026-02-17
SmartLoader campaign discovered by STAR Labs
2026-02-17
Fake Oura MCP server identified as malware distribution method
More articles in this cluster (2)
Following this threat?
Track StealC in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 FakeGit Malware Campaign Resurfaces with 17,610 Malicious Repositories The FakeGit malware campaign has reactivated, distributing SmartLoader malware via over 17,610 fake repositories on GitHub. This resurgence, noted by researchers from Apiiro, began on October 4, 2026, and has already seen the creation of more than 13,000 repositories in just 34 hours. The malicious repositories employ…
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…