 Newswise
SpaceX's Starship Achieves Orbital Milestone with Starlink V3 Deployment
Article Content

- •SpaceX's Starship reached orbit and deployed Starlink V3 satellites on September 29, 2026.
- •The mission's success could lower launch costs significantly, benefiting major customers like NASA.
- •Challenges remain for future lunar missions, including landing and orbital refueling.
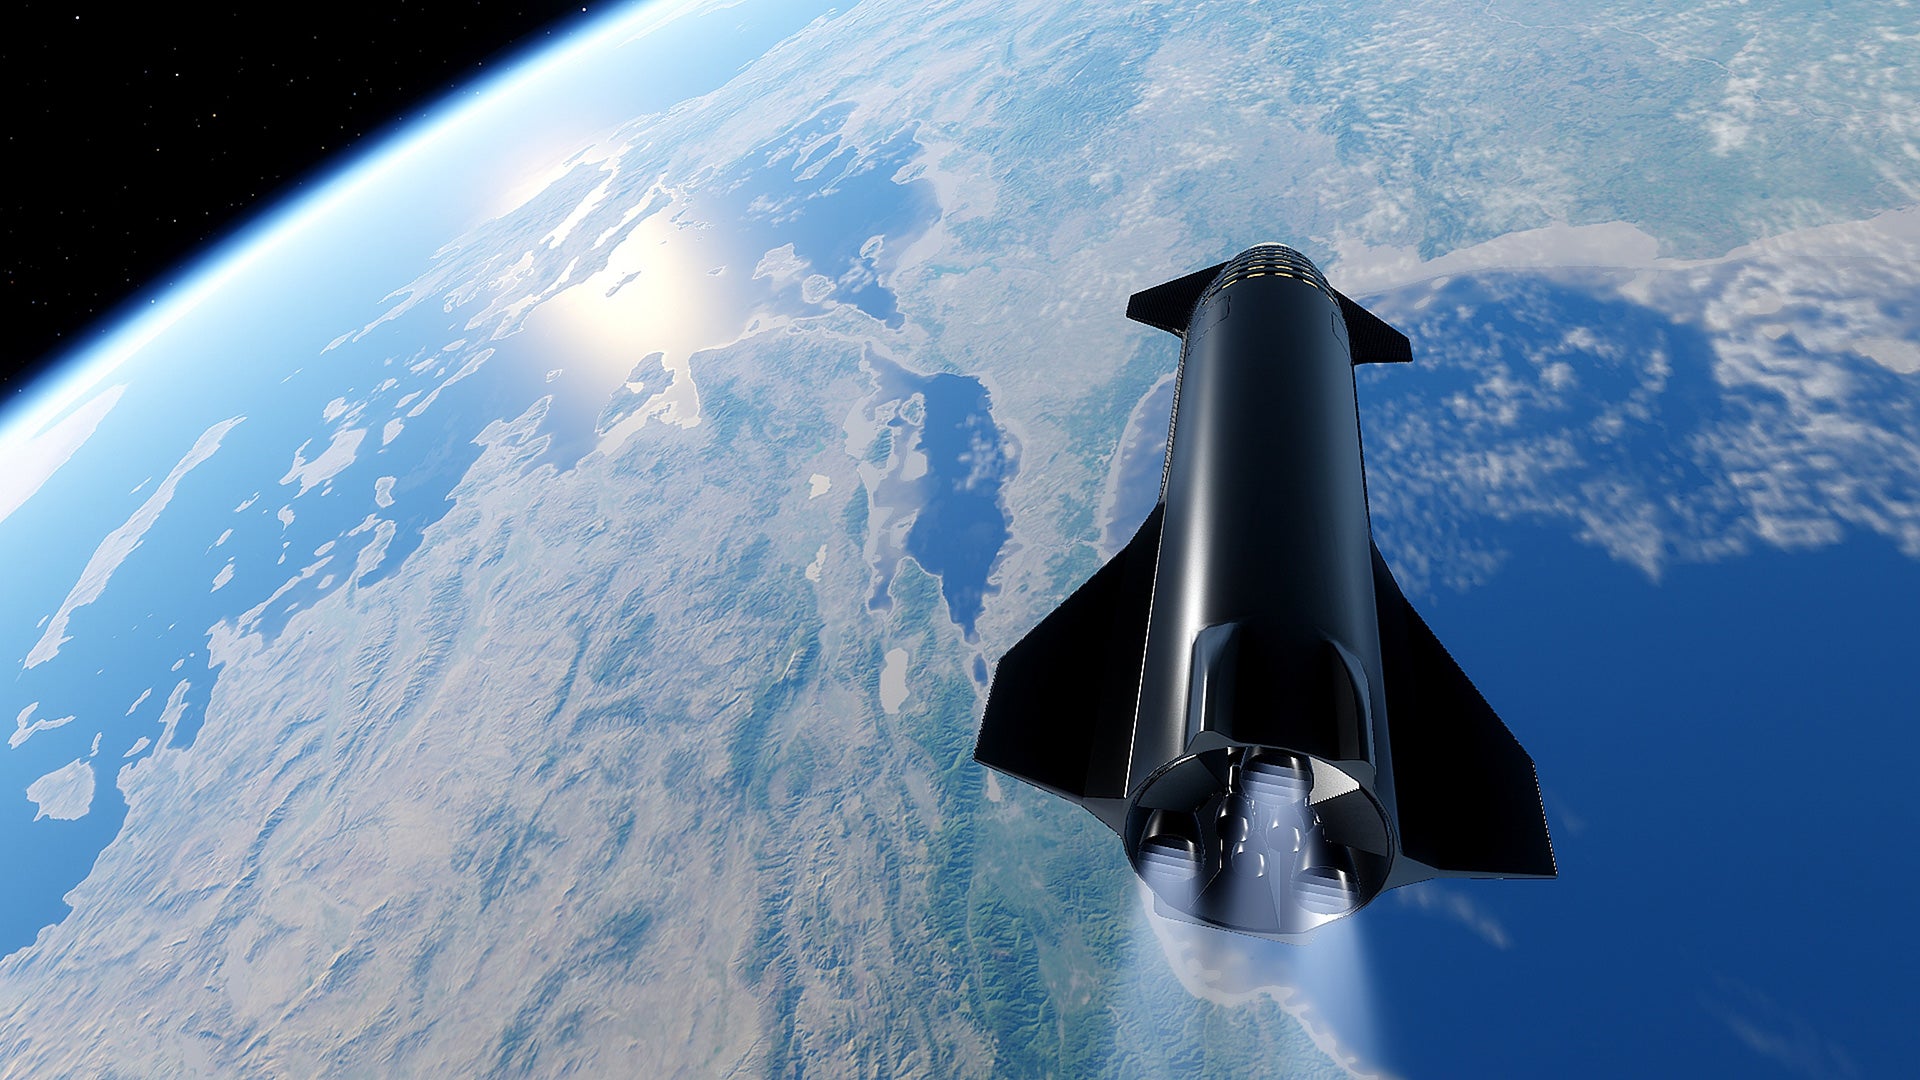
On September 29, 2026, SpaceX’s Starship successfully reached orbit and deployed its first batch of Starlink V3 satellites. This event marks a significant advancement in the commercial space sector, impacting launch economics and federal contracting. Jon Crocker from the University of Maryland's Robert H. Smith School of Business highlighted that the mission, although cut short due to a partial engine failure, demonstrates the potential for cost reductions in payload delivery. The immediate beneficiaries of this milestone include SpaceX’s Starlink and priority customers like NASA and the Space Force. However, the launch's limitations may lead to increased prices for companies lacking their own launch capabilities. While this achievement is promising for future lunar missions under NASA's Artemis program, significant engineering challenges remain, including orbital refueling and landing on the Moon. Overall, this event is seen as a pivotal moment in the evolution of space commerce and defense procurement.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…