 Hackread
SPECTER Attack Exploits USB Power Signals for Data Exfiltration
Article Content

- •SPECTER enables covert data exfiltration from air-gapped systems via USB power signals.
- •Requires malware with administrative privileges to manipulate USB control operations.
- •Demonstrated signaling rates are low, limiting the attack's scope to short sensitive data.
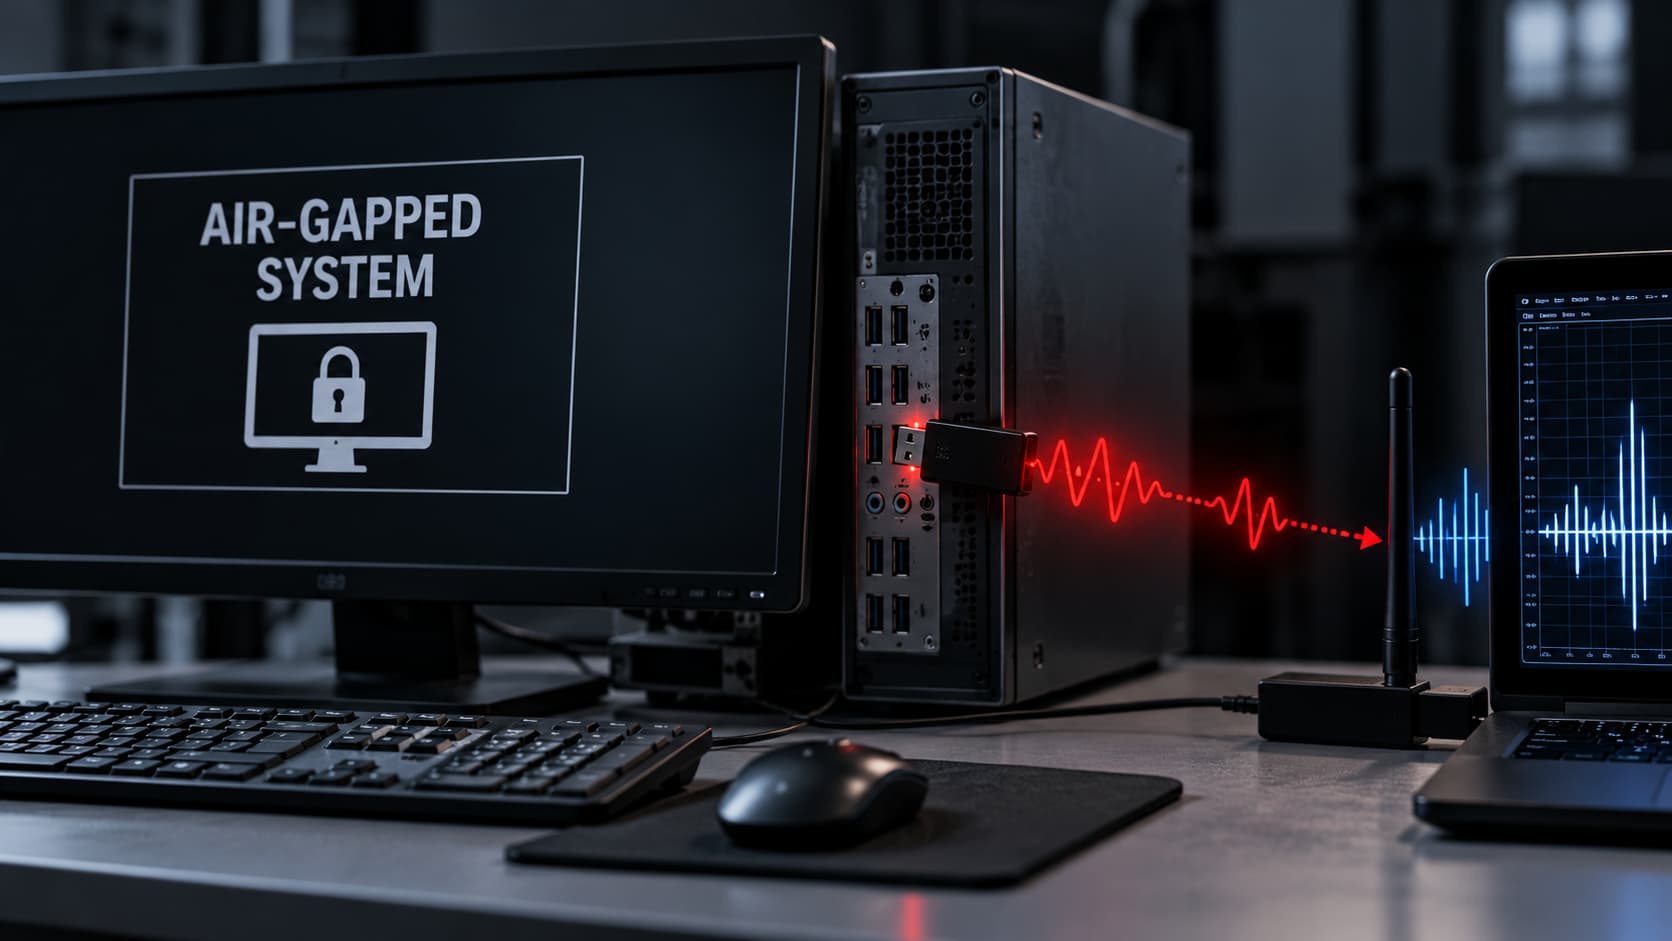
Researchers from Korea University have unveiled SPECTER, a covert channel that enables malware to extract sensitive data from air-gapped systems by manipulating USB power-management settings. This technique requires root or administrator access on the compromised host and encodes information through USB operations without using traditional data transfers. The researchers demonstrated the method on Windows 10 and Ubuntu 22.04, achieving data signaling rates of 0.2 to 0.25 bits per second via smartphone charging states and 1 bit per second through peripheral behavior, such as a USB mouse. Additionally, they explored near-field RF activity for signal recovery using a software-defined radio. While SPECTER is not suitable for large data transfers, it poses a risk for extracting short, sensitive secrets like credentials. The findings emphasize the need for heightened security awareness regarding USB power-management events.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Korea University in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What systems are affected by SPECTER?
How urgent is this threat?
What can organizations do to mitigate this risk?
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…