 Subtelforum
SUBCO Plans Investment in Subsea Infrastructure with Cable Ship and Survey Drone
Article Content

- •SUBCO is considering a USV for cable surveys and a cable-laying ship.
- •The cable-laying vessel could cost US$165 million, with delivery by 2029.
- •Government funding from the US and Australia is anticipated to support these projects.
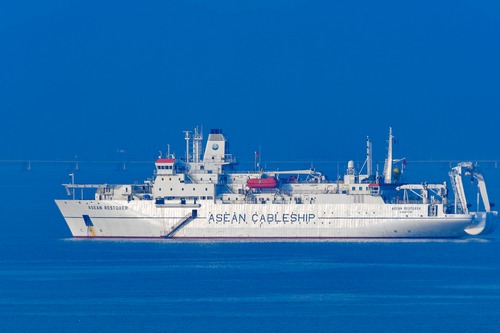
SUBCO is evaluating the purchase of an uncrewed surface vessel (USV) for cable-route surveys and a dedicated cable-laying ship, as announced by founder Bevan Slattery at the AusNOG conference. The USV could be owned or leased, with a target delivery date of December 2027, while the cable-laying vessel is estimated to cost around US$165 million and could be delivered by the end of 2029. SUBCO aims to enhance Australia's subsea infrastructure capabilities, which currently lack a dedicated cable-laying vessel. Slattery indicated that government contributions from the US and Australia would be sought to support these investments. A decision on the cable-laying vessel is expected by the end of 2026. The initiatives are still under evaluation and not yet committed.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What is the expected cost of the cable-laying vessel?
When will a decision be made on the cable-laying vessel?
What capabilities will the USV provide?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…