 Railway.Supply
Successful BVLOS Drone Trial Enhances Rail Incident Response Capabilities
Article Content

- •Project SOCNI tested BVLOS drone operations for rail incident response and inspections.
- •The trial involved multiple organizations ensuring safe airspace sharing among drones.
- •Results will inform the development of NATS' OpenAir concept for airspace integration.
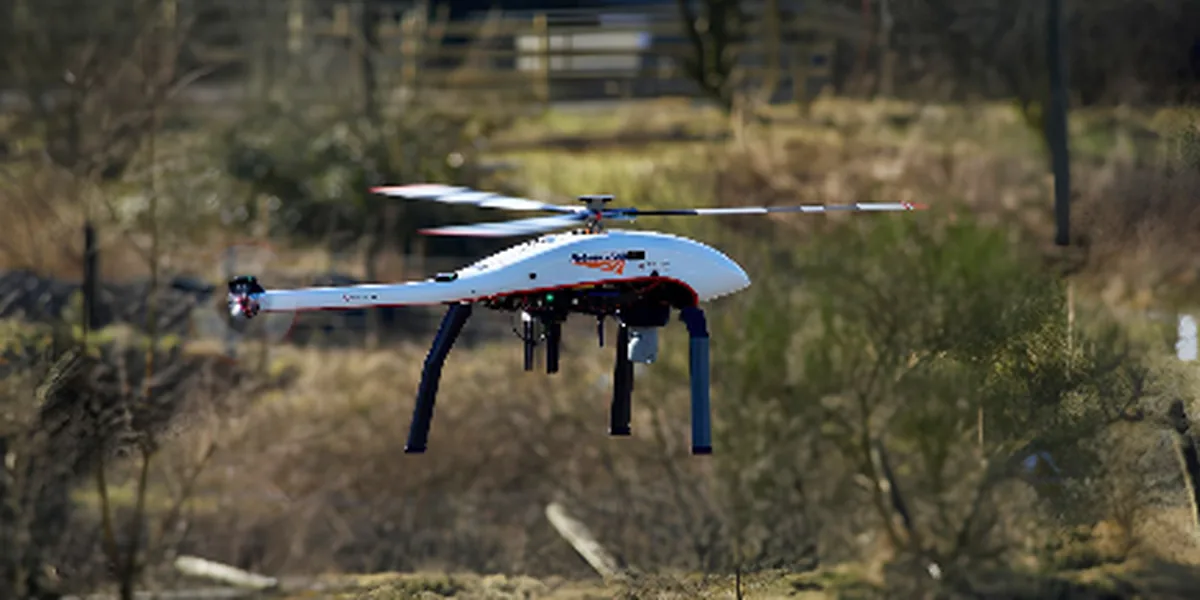
NATS, DroneCloud, and Network Rail completed Project SOCNI, which tested beyond visual line of sight (BVLOS) drone operations around critical national infrastructure, focusing on rail inspections and incident response. The project involved multiple partners, including Transport for Wales and British Transport Police, and aimed to ensure safe coexistence of multiple drone operators in the same airspace. The live demonstration utilized real aircraft and simulated scenarios to validate safety protocols and data sharing. The outcomes are expected to inform the development of NATS' OpenAir concept, which facilitates the integration of new airspace users. The project was supported by the UK Research and Innovation Future Flight programme, highlighting its significance in advancing drone operations in complex environments. Future demonstrations will build on the findings from SOCNI to further enhance operational safety and efficiency.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…