 Abc7Chicago
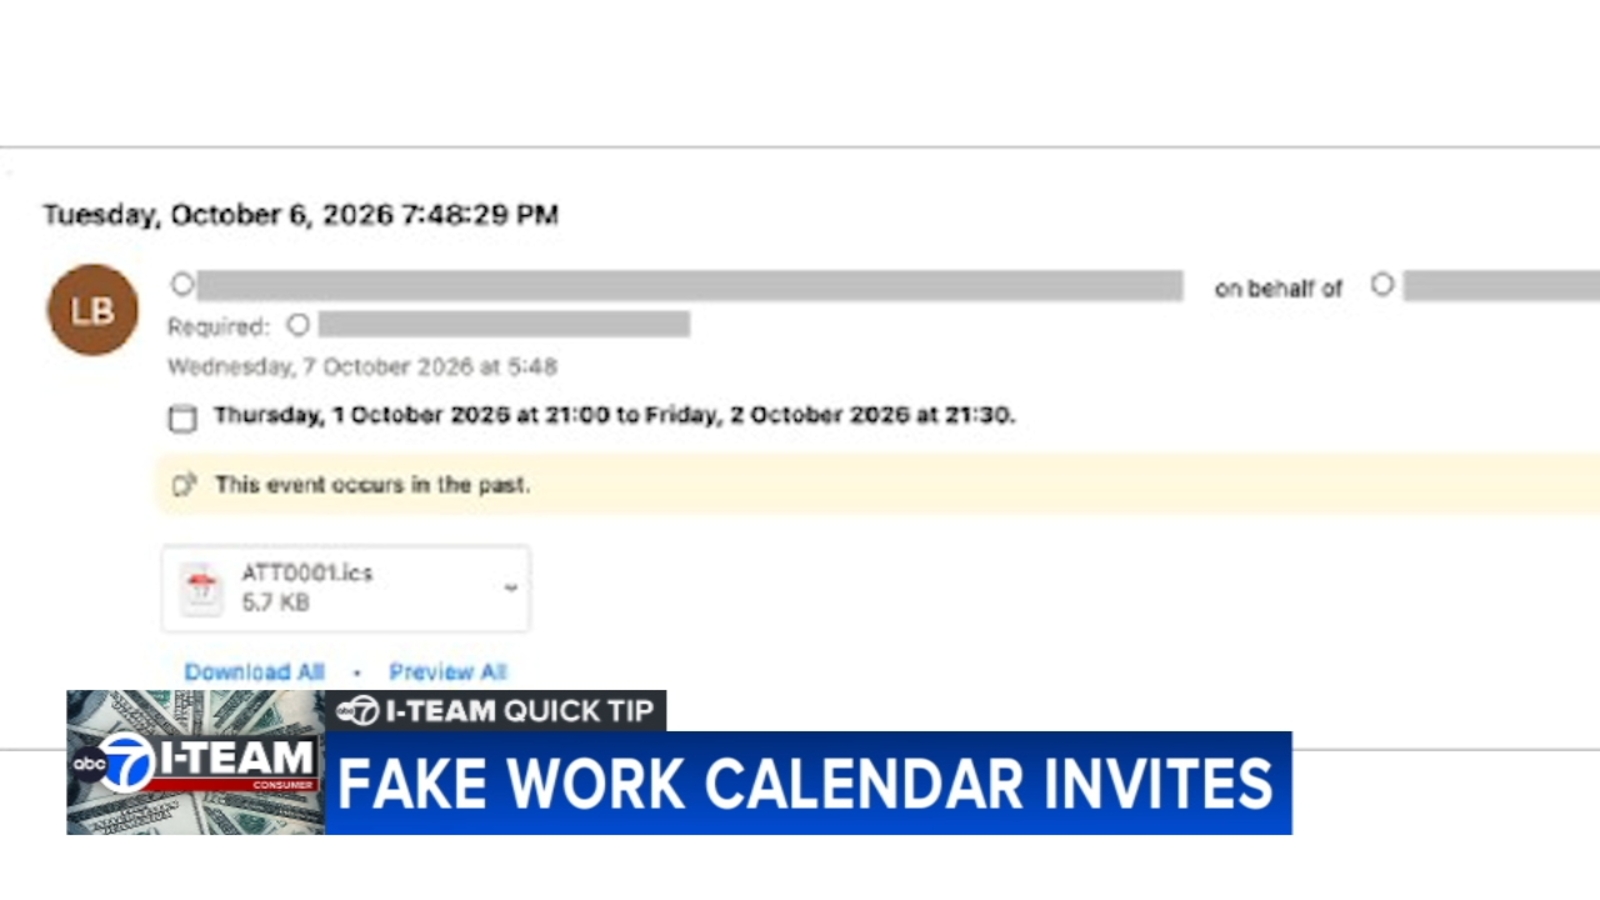
Surge in Phishing Scams via Calendar Invites
Article Content

- •Calendar invite phishing scams have surged by 1,216% from July to August 2026.
- •Over 302,000 phishing emails targeting 40,000 organizations have been reported.
- •Users are advised to verify invite sources and scrutinize links before clicking.
Cybersecurity researchers have reported a significant increase in phishing scams using fake calendar invites to steal credentials. These scams exploit the trust associated with calendar events, often appearing to come from known services or internal sources. Over 302,000 phishing emails targeting more than 40,000 organizations have been flagged, with calendar invites accounting for nearly 20% of callback phishing attempts in late 2025. The urgency created by these invites prompts users to click on malicious links or attachments. Security experts emphasize the importance of verifying the sender and scrutinizing links before interacting with calendar invites. The rise in these scams has been dramatic, with a reported increase of 1,216% in attacks from July to August 2026. This trend highlights the evolving tactics of cybercriminals in their phishing strategies.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
How can I identify a fake calendar invite?
What should I do if I receive a suspicious invite?
Are there specific tools to help detect these scams?
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…