 Turkiyetoday
Türkiye and Germany Revive Strategic Dialogue Amid EU Accession Discussions
Article Content

- •Türkiye and Germany are reviving their Strategic Dialogue Mechanism after 12 years.
- •Fidan urged the EU to separate Türkiye's accession process from political issues.
- •Bilateral trade between Türkiye and Germany is projected to reach $60 billion soon.
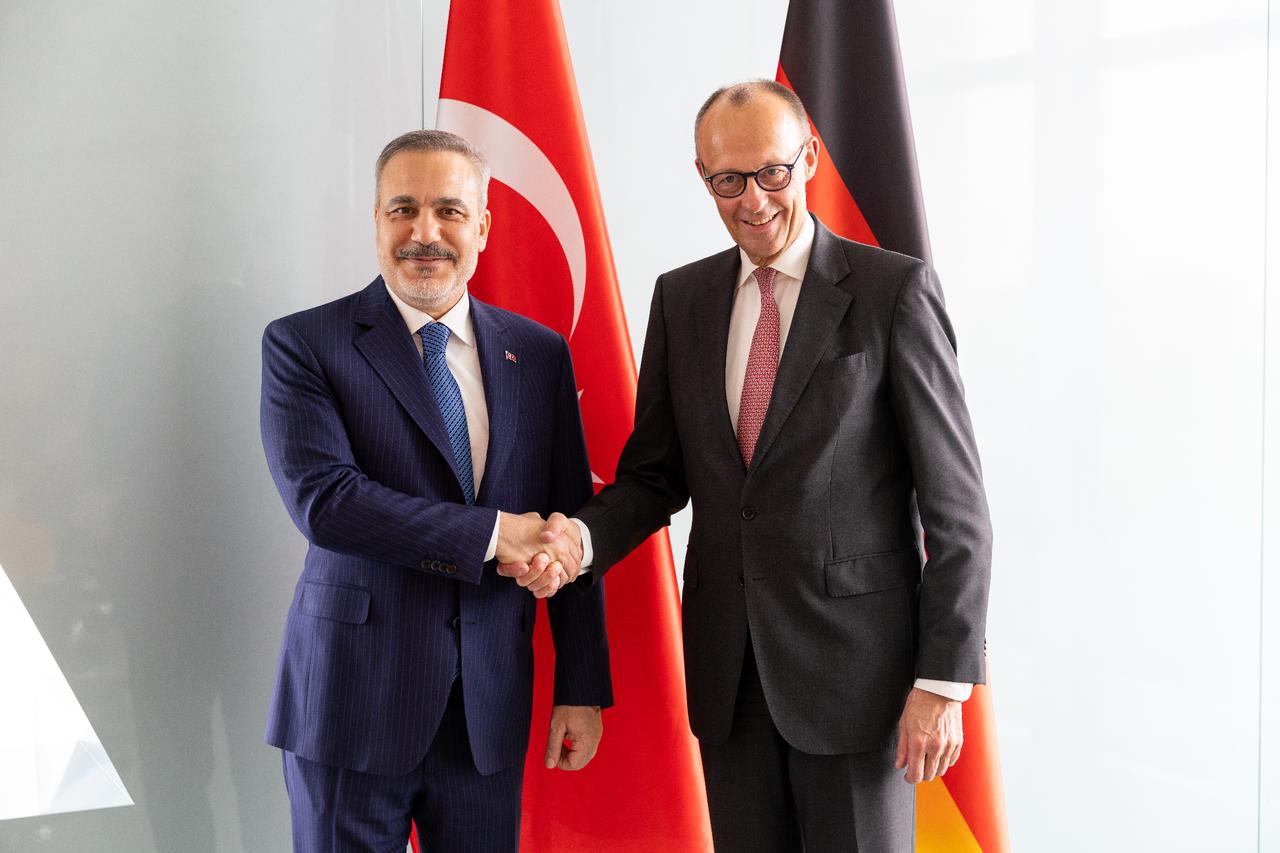
On May 18, 2026, Turkish Foreign Minister Hakan Fidan met with German officials in Berlin to revive the Türkiye-Germany Strategic Dialogue Mechanism after 12 years. This mechanism aims to address strategic issues, including security and defense cooperation, and is a response to improved bilateral relations. Fidan emphasized the need for the EU to decouple Türkiye's accession process from political motivations, arguing that exclusion from EU defense frameworks undermines European security goals. The bilateral trade between Türkiye and Germany is currently around $52 billion, with aspirations to reach $60 billion. The discussions also included Türkiye's defense industry cooperation and the modernization of the customs union with the EU. Fidan's visit comes amid ongoing regional tensions, including conflicts involving Iran and Israel, which were also addressed during the talks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…