Article Content
Browse articles 
- •Türkiye and Syria both deny claims of a meeting between their officials and Hezbollah.
- •The Turkish Communications Directorate described the allegations as entirely fabricated.
- •Both governments warned the public against misinformation from unofficial sources.
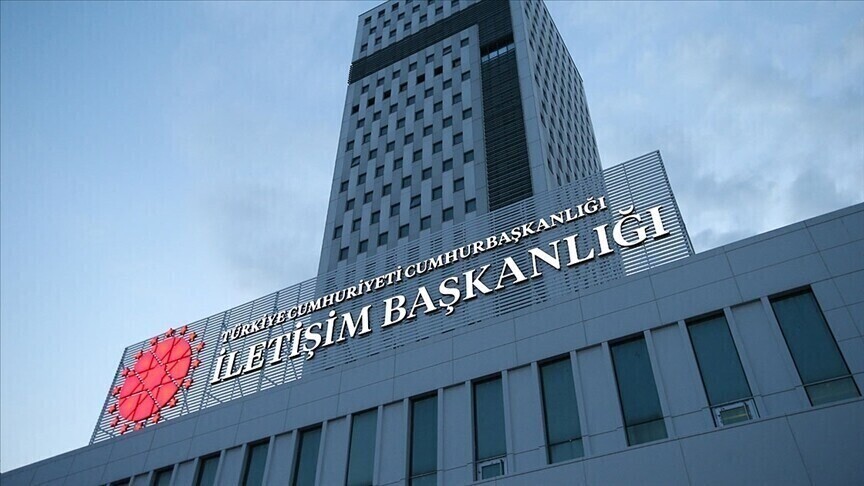
On October 1, 2026, Türkiye and Syria rejected claims that officials from the Syrian government and Hezbollah met in Türkiye. The Turkish Communications Directorate’s Center for Combating Disinformation stated that these allegations were entirely unfounded and fabricated. They emphasized that the claims regarding the meeting's date, venue, content, and participants do not reflect reality. The Syrian government also denied the meeting, asserting that the claims were false. Both governments urged the public to rely on official statements and warned against misinformation circulating through unofficial channels.
Ask AI about this cluster
Answers cite the sources they use
Updated 8h ago How this analysis works
Timeline
2026-10-01
Claims of meeting rejected
Türkiye and Syria issued statements denying that Syrian government and Hezbollah officials met in Türkiye.
Aa.TrMore articles in this cluster (2)
Common questions
What claims were made about the meeting?
Reports claimed that Syrian government officials and Hezbollah representatives met in Türkiye, which both governments denied.
What actions did Türkiye take in response?
Türkiye's Communications Directorate issued a statement rejecting the claims as false and urged reliance on official sources.
How did Syria respond to the allegations?
The Syrian government also denied the meeting, calling the claims false and fabricated.
Continue Reading
 Citrix NetScaler Critical Vulnerabilities Exploited: Urgent Patching Required Citrix NetScaler ADC and Gateway products are affected by critical vulnerabilities CVE-2026-88771 and CVE-2026-88772, both assigned a CVSS score of 9.5. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on September 27, 2026, and mandated…
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…