 www.straitstimes.com
Thailand Seizes $1.5 Billion in Cyber-Crime Assets Linked to Scam Operations
Article Content

- •Thai authorities seized $1.5 billion linked to a major money-laundering scheme.
- •The operation involved fake investment scams targeting victims in Southeast Asia.
- •Arrest warrants were issued for key figures, including Ben Smith and his associates.
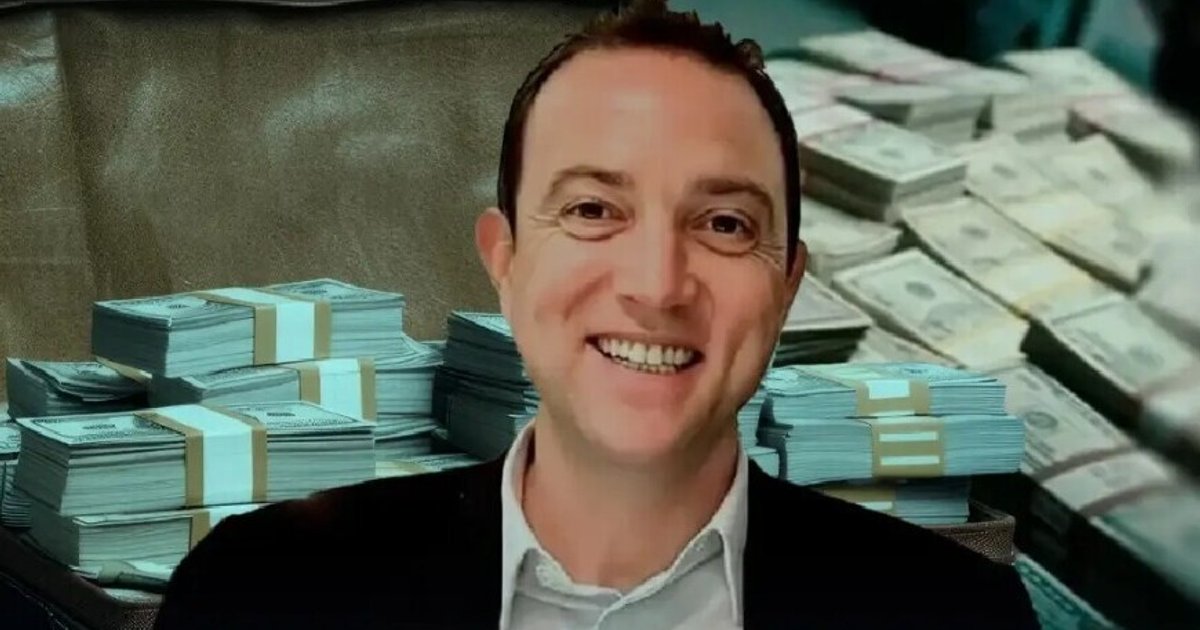
Thai authorities have seized or frozen assets worth approximately $1.5 billion, linked to a major money-laundering scheme involving Cambodian cyber-scam operations. The scheme, allegedly led by South African businessman Ben Smith, also known as Benjamin Mauerberger, involved luring victims into fake investment schemes. Arrest warrants have been issued for Smith, his Thai wife Cattaliya Beevor, Cambodian businessman Yim Leak, and four others. The funds were reportedly moved through Cambodian banks and overseas investment firms to acquire stakes in companies listed on the Thai stock exchange. Investigators uncovered a complex network that utilized personal and corporate accounts to launder money over several years. The operation was exposed following a two-year investigation by a team reporting through a website called Whale Hunting. The seized assets may be used to compensate scam victims, but the case has sparked legal disputes regarding the media coverage and business impacts.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Common questions
Who are the main individuals involved?
What types of assets are being seized?
How will the seized assets be used?
Continue Reading
 North Korean Hackers Steal $6.3 Billion from Binance in Record Crypto Heist On October 29, 2026, Binance, the world's largest cryptocurrency exchange, reported a massive security breach resulting in the theft of approximately $6.3 billion across ten blockchains. The attack is attributed to North Korea's TraderTraitor hacking group, which gained access via a compromised DevOps engineer's…
 Chinese Actor Compromises US Government Networks via PHP2Shell Exploit A suspected Chinese nation-state actor exploited vulnerabilities in Palo Alto Networks firewalls using a chained PHP2Shell exploit and a Linux kernel privilege escalation flaw. The attack, which began on October 23, targeted 25 servers across the US, Japan, Taiwan, and South Korea, with a focus on US…