 www.army.mil
Army Activates Multi-Domain Command-Pacific for Enhanced Operations
Article Content

- •MDC-PAC combines the 7th Infantry Division and the 1st MDTF for enhanced operational capabilities.
- •The command operates independently to synchronize multidomain effects across the Indo-Pacific.
- •Lessons from global conflicts, including drone warfare, informed the development of MDC-PAC.
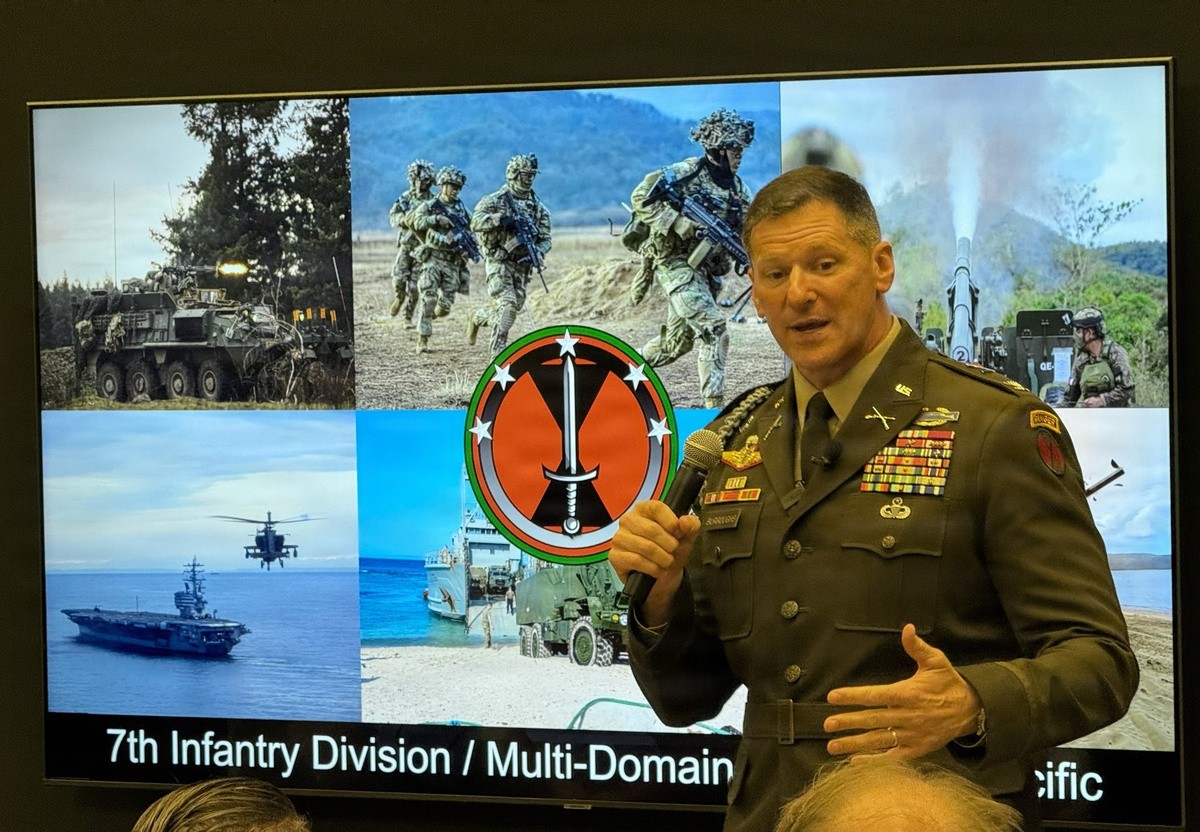
On June 18, 2026, the U.S. Army officially activated the Multi-Domain Command-Pacific (MDC-PAC), merging the 7th Infantry Division and the 1st Multi-Domain Task Force. This new command aims to enhance theater-level operations in the Pacific by integrating maneuver formations with advanced capabilities in cyber, space, electronic warfare, and intelligence. The MDC-PAC was established following a successful operational experiment conducted in December 2024, which validated the effectiveness of a two-star headquarters for multidomain operations. The command is designed to operate independently, providing a covering force for joint operations, and consists of 12,000 soldiers across various brigades and battalions. The initiative reflects lessons learned from global conflicts, particularly the use of drones for reconnaissance and targeting. The Army aims to position itself as a relevant force in potential conflicts in the Pacific region, particularly against adversaries like China.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…