 Unn.Ua
TikTok Removes Over 1,000 Posts Linked to Russian Alabuga Drone Production
Article Content

- •TikTok removed over 1,000 posts linked to Alabuga for violating platform rules.
- •Six accounts were blocked for exploitation, with actions taken against more than 40 accounts.
- •Alabuga is a key site for the production of Shahed/‘Geran’ drones used in attacks.
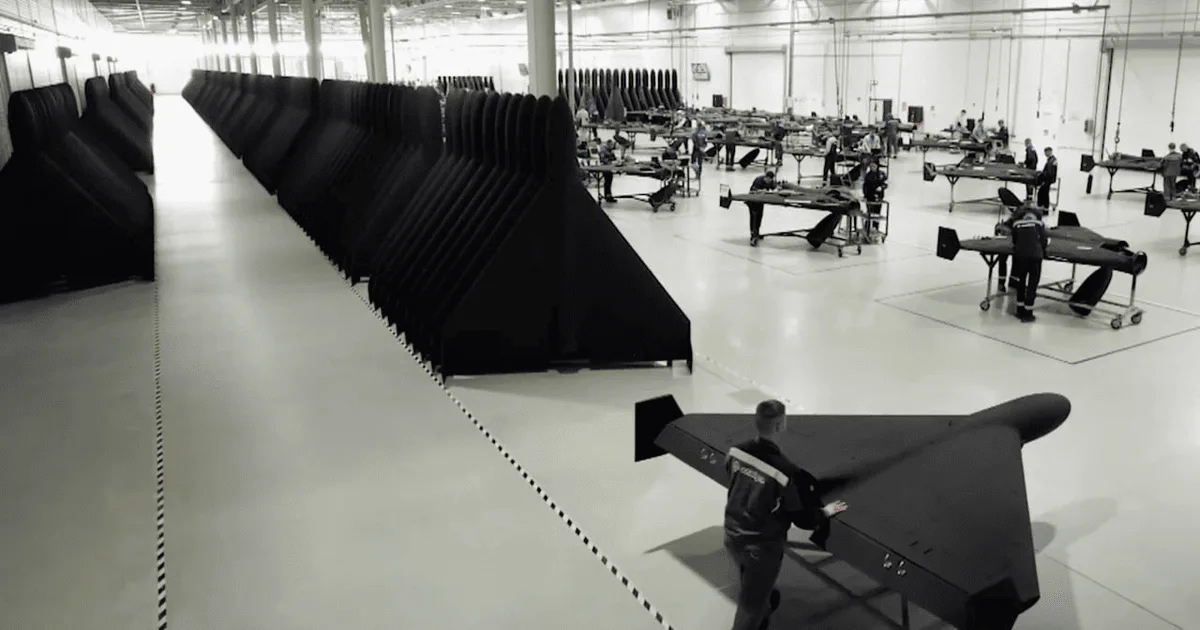
TikTok has taken down more than 1,000 posts related to Russia's Alabuga Special Economic Zone, where Shahed/‘Geran’ attack drones are manufactured. The removal was prompted by requests from the Center for Countering Disinformation, which reported that the content violated platform rules. Additionally, TikTok blocked six accounts for exploiting individuals and took action against over 40 accounts in total. The social network has reportedly enhanced its systems for detecting such content to prevent re-uploads. An ongoing investigation is looking into a potential network of accounts associated with this content. Alabuga is significant as it has become a center for drone production used in attacks against Ukrainian cities. YouTube previously removed around 600 videos promoting the Alabuga drone factory.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Alabuga in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What content was removed from TikTok?
What is Alabuga known for?
What actions were taken against accounts?
Continue Reading
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…
 Critical Authentication Bypass in Rejetto HFS Exploited Within 24 Hours Anthropic's Mythos model identified a critical authentication bypass in Rejetto HTTP File Server (HFS), tracked as CVE-2026-61500, allowing remote code execution. Discovered by Horizon3 researcher Zach Hanley, the flaw was revealed on September 27, 2026, and exploitation began within 24 hours, with attacks traced to…