 www.em.com.br
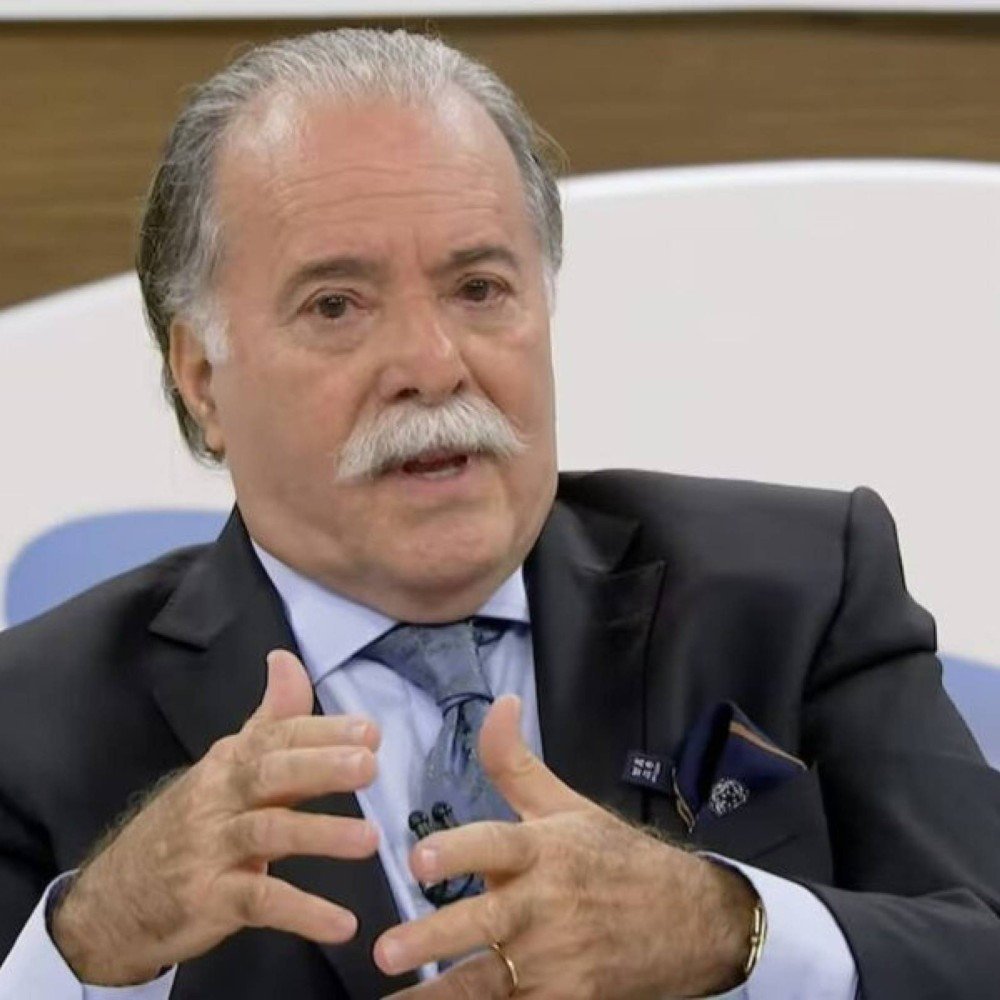
Tony Ramos Criticizes AI Use in Recreating Actors
Article Content

- •Tony Ramos opposes AI recreating actors, calling it deceptive.
- •He was a victim of a deepfake used for unauthorized advertising.
- •Ramos stresses the importance of human essence in art over technology.
Tony Ramos publicly condemned the use of artificial intelligence to recreate actors during an interview on 'Roda Viva' on September 28, 2026. He stated that he would never allow his image to be recreated by AI, calling it a deception to audiences. Ramos shared that he was recently a victim of a deepfake, where his likeness was used to promote prostate medication without his consent. He emphasized that true artistic quality comes from human essence, not technology. Ramos acknowledged that AI is here to stay and highlighted the need to learn how to manage its implications, which he believes could lead to criminal activities. He left the decision regarding the use of his image after death to his family. The discussion reflects ongoing debates about AI's role in the entertainment industry.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What did Tony Ramos say about AI recreations?
How was Ramos affected by a deepfake?
What are Ramos's views on the future of AI?
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…