 www.smh.com.au
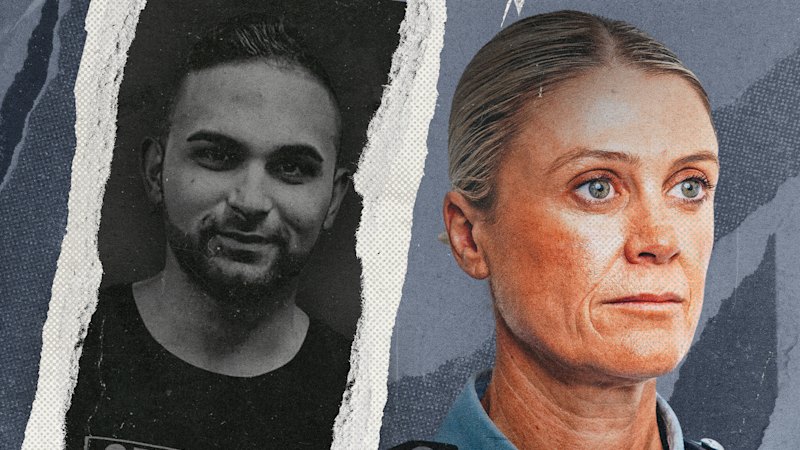
Top Cop Prioritizes Capture of Dural Caravan Hoaxer Amid Rising AI Crime Threats
Article Content

- •Sayit Akca is the AFP's top target for orchestrating the Dural caravan hoax.
- •The AFP is developing AI tools to combat online child exploitation and improve reporting mechanisms.
- •Barrett emphasizes the need for international cooperation to tackle organized crime enhanced by AI.
Australian Federal Police Commissioner Krissy Barrett has identified Sayit Akca, the alleged mastermind behind the 2025 Dural caravan hoax, as a top priority for capture. Akca is believed to have orchestrated a terror plot targeting Sydney's Jewish community, leading to heightened security concerns. Barrett highlighted the increasing use of artificial intelligence in facilitating online crimes, particularly against children, with a significant number of adolescents reporting abuse incidents to AI chatbots. The AFP is partnering with Monash University to develop AI tools aimed at detecting online predators. Barrett's comments come as the agency expands its overseas operations to combat organized crime enhanced by technology. The Dural caravan hoax incident, discovered in January 2025, involved explosives and raised fears of potential attacks in Sydney. Akca has been on the run since mid-2023 after fleeing Australia on drug charges.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Common questions
What is the Dural caravan hoax?
What actions is the AFP taking against Akca?
How is AI being used to combat online crime?
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…