 www.theguardian.com
Trump Announces Deployment of 5,000 Troops to Poland Amid NATO Tensions
Article Content

- •Trump announced an additional 5,000 US troops to Poland amid NATO tensions.
- •The Pentagon recently halted a planned rotation of 4,000 troops to Poland.
- •Concerns rise among Polish leaders regarding US military commitments in light of Russian aggression.
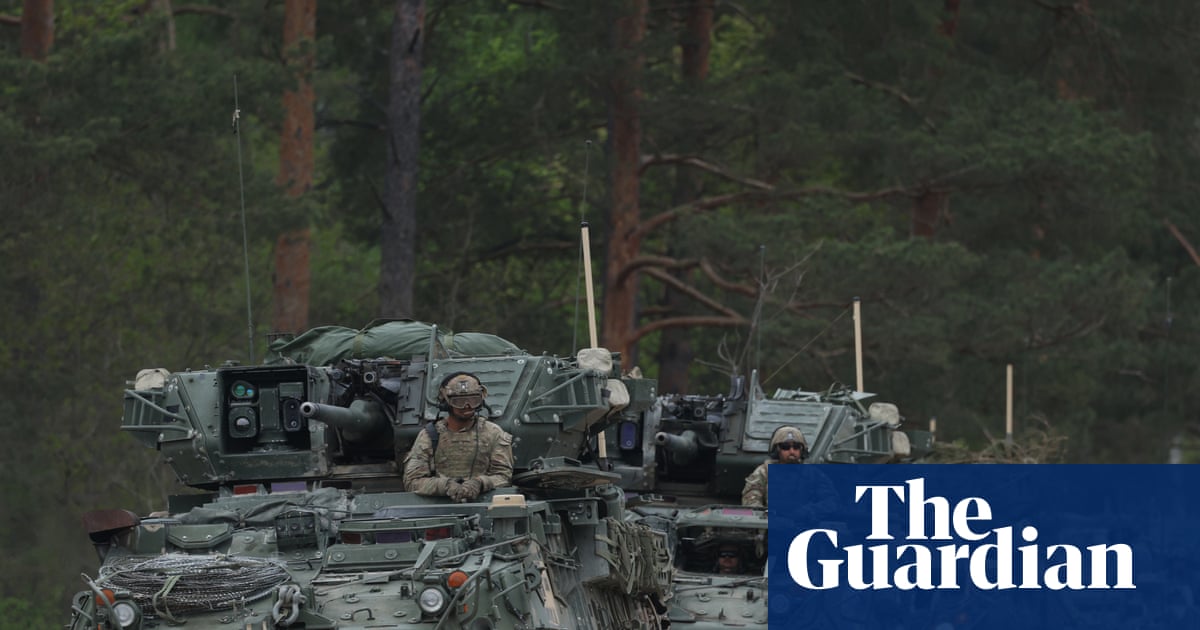
On May 22, 2026, US President Donald Trump announced the deployment of an additional 5,000 troops to Poland, coinciding with NATO foreign ministers' upcoming meeting. This decision follows the Pentagon's recent halt of a planned troop rotation of 4,000 soldiers to Poland, raising concerns among Polish leaders about the assertive Russian stance amid the ongoing war in Ukraine. The announcement marks a significant shift in US military posture in Europe, especially after Trump had previously criticized NATO allies for not supporting US actions in Iran. The deployment's nature—whether permanent or rotational—remains unclear. The situation reflects ongoing tensions between the US and its NATO allies, particularly regarding military support and defense responsibilities. The announcement has drawn mixed reactions, with some Polish officials expressing anxiety over the shifting US commitments. The US currently has around 10,000 troops stationed in Poland.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…