 Thebulwark
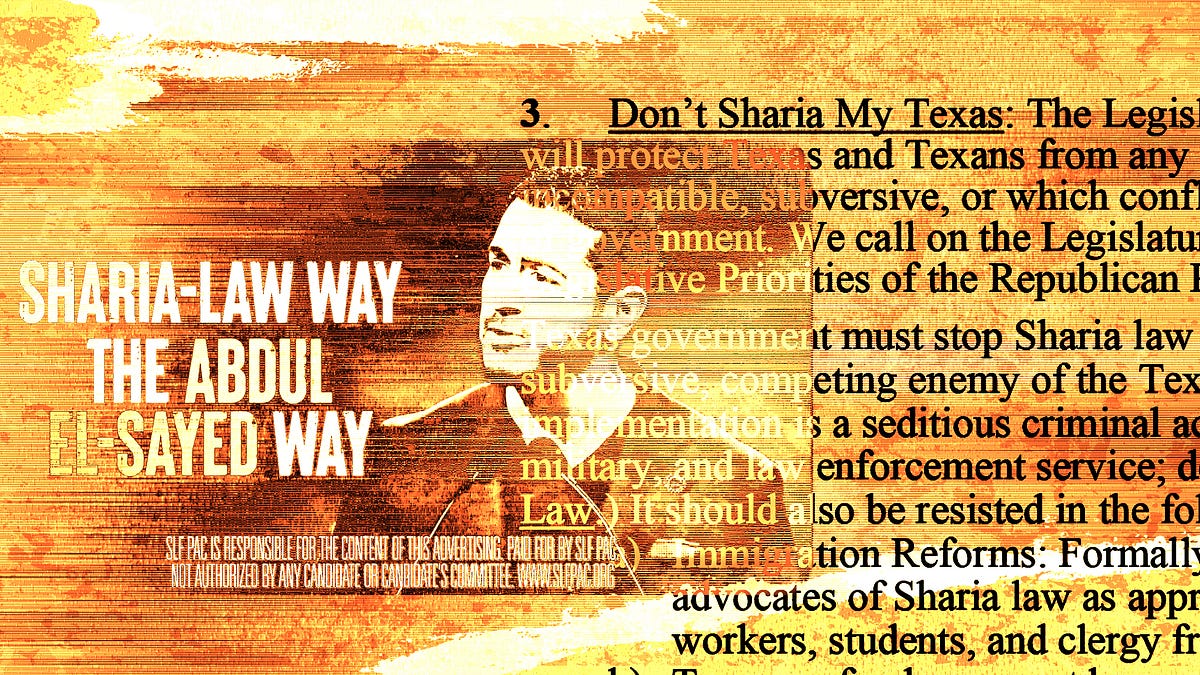
Trump Intensifies Anti-Muslim Rhetoric Against Abdul El-Sayed
Article Content

- •Trump labeled Abdul El-Sayed a 'jihadist' and questioned his loyalty to the U.S.
- •El-Sayed's campaign is seen as a critical race for control of the Senate.
- •The rhetoric against El-Sayed reflects a broader trend of anti-Muslim sentiment in politics.
In the lead-up to the midterm elections, President Donald Trump escalated his anti-Muslim rhetoric against Michigan Senate candidate Abdul El-Sayed, labeling him a 'jihadist' and questioning his loyalty to the U.S. Trump's remarks drew condemnation from former allies and highlighted a broader Republican strategy that exploits anti-Muslim sentiments. El-Sayed, who could become the first Muslim senator, has denied any ties to extremist groups and criticized the attacks as shameful. The Michigan Senate race is pivotal for control of the chamber, with Republicans facing challenges on economic issues. Trump's comments included references to the September 11 attacks, aiming to frame El-Sayed as a national security threat. The campaign against El-Sayed reflects a troubling trend in U.S. politics, where fear and misinformation about Muslims are increasingly weaponized for electoral gains.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (9)
Common questions
What specific accusations has Trump made against El-Sayed?
How has El-Sayed responded to these attacks?
What is the significance of the Michigan Senate race?
Continue Reading
 .NET Vulnerability CVE-2026-111497 Requires Immediate Action On October 25, 2026, Microsoft released out-of-band security updates for.NET addressing CVE-2026-111497, a vulnerability in the Brotli decompression algorithm that allows unauthorized attackers to elevate privileges over a network. The flaw affects.NET versions 8, 9, 10, and 11, particularly in applications that…
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…