 En.Bloomingbit
Trump Warns of 50% Tariffs for Exploiting Companies Ahead of Midterm Elections
Article Content

- •Trump warns of potential 50% tariffs for companies exploiting the U.S. market.
- •The comments aim to bolster support for his administration ahead of midterm elections.
- •No specific companies or exploitation methods were identified in the warnings.
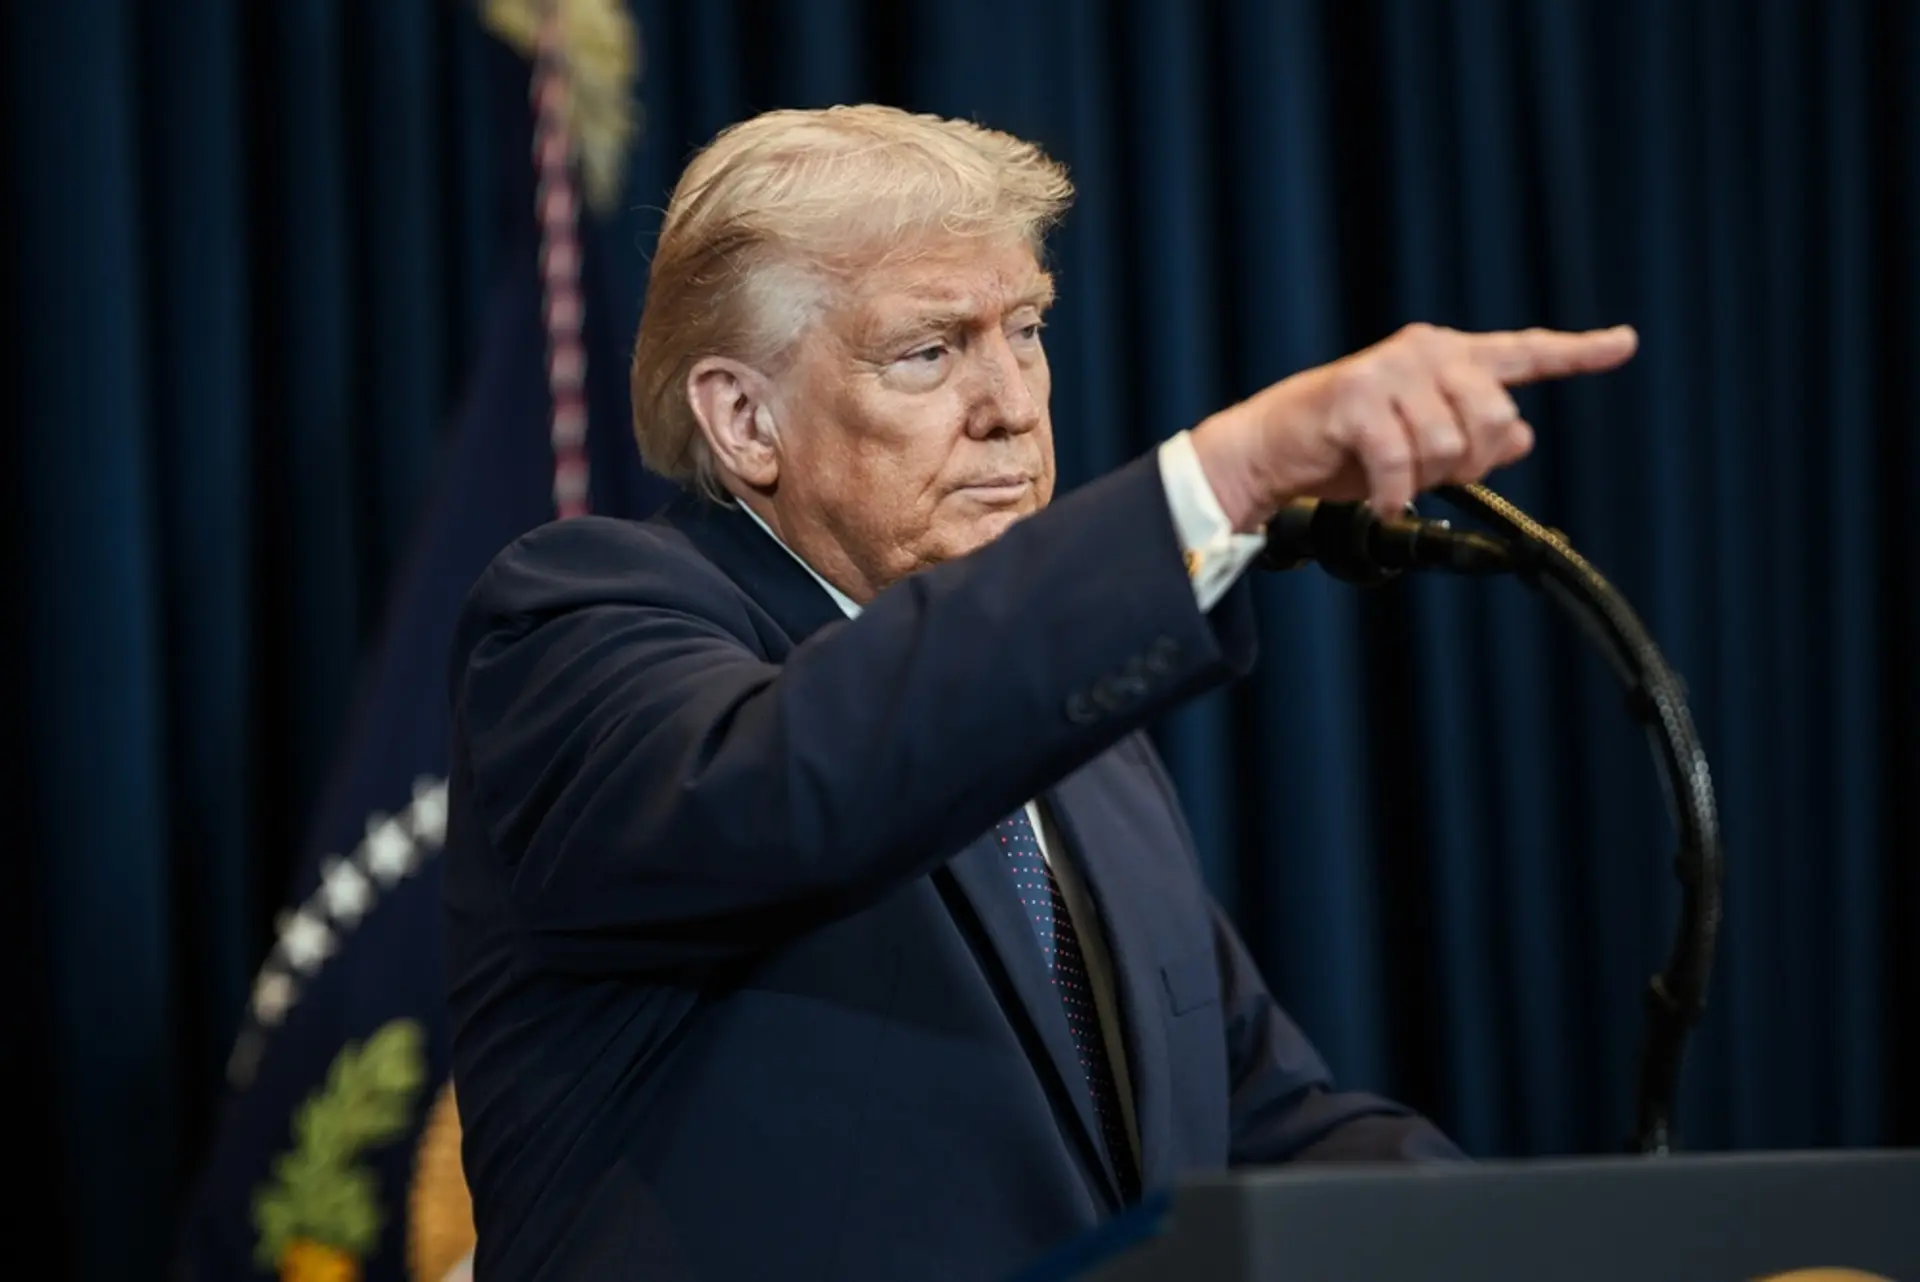
On October 25, 2026, President Donald Trump warned that tariffs could increase to 50% for foreign companies exploiting the U.S. market. This statement was made during a Fox News interview, where he criticized Japan, South Korea, and China for undermining the U.S. auto industry. Trump claimed that companies are returning to the U.S. to avoid a 25% tariff, although he did not specify which companies or how they were exploiting the system. His remarks are seen as an effort to reinforce his commitment to protecting American industries ahead of the upcoming midterm elections. Additionally, Trump hinted at possible military action against Iran, suggesting a choice between diplomacy and decisive action. The market is concerned about potential oil price increases if military action occurs. No specific examples of exploitation were provided, and the situation remains under scrutiny as the elections approach.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What companies are at risk of the new tariffs?
How might this impact the U.S. economy?
What is the timeline for potential military action against Iran?
Continue Reading
 .NET Vulnerability CVE-2026-111497 Requires Immediate Action On October 25, 2026, Microsoft released out-of-band security updates for.NET addressing CVE-2026-111497, a vulnerability in the Brotli decompression algorithm that allows unauthorized attackers to elevate privileges over a network. The flaw affects.NET versions 8, 9, 10, and 11, particularly in applications that…
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…