 Abc7
Trump Suggests Iran Could Attack Major US Cities Amid Backlash
Article Content

- •Trump's remarks about Iran targeting US cities sparked outrage from California officials.
- •Governor Newsom described Trump's comments as 'deranged and dangerous,' highlighting the potential threat to millions.
- •The White House defended Trump, claiming he was emphasizing the importance of preventing a nuclear threat from Iran.
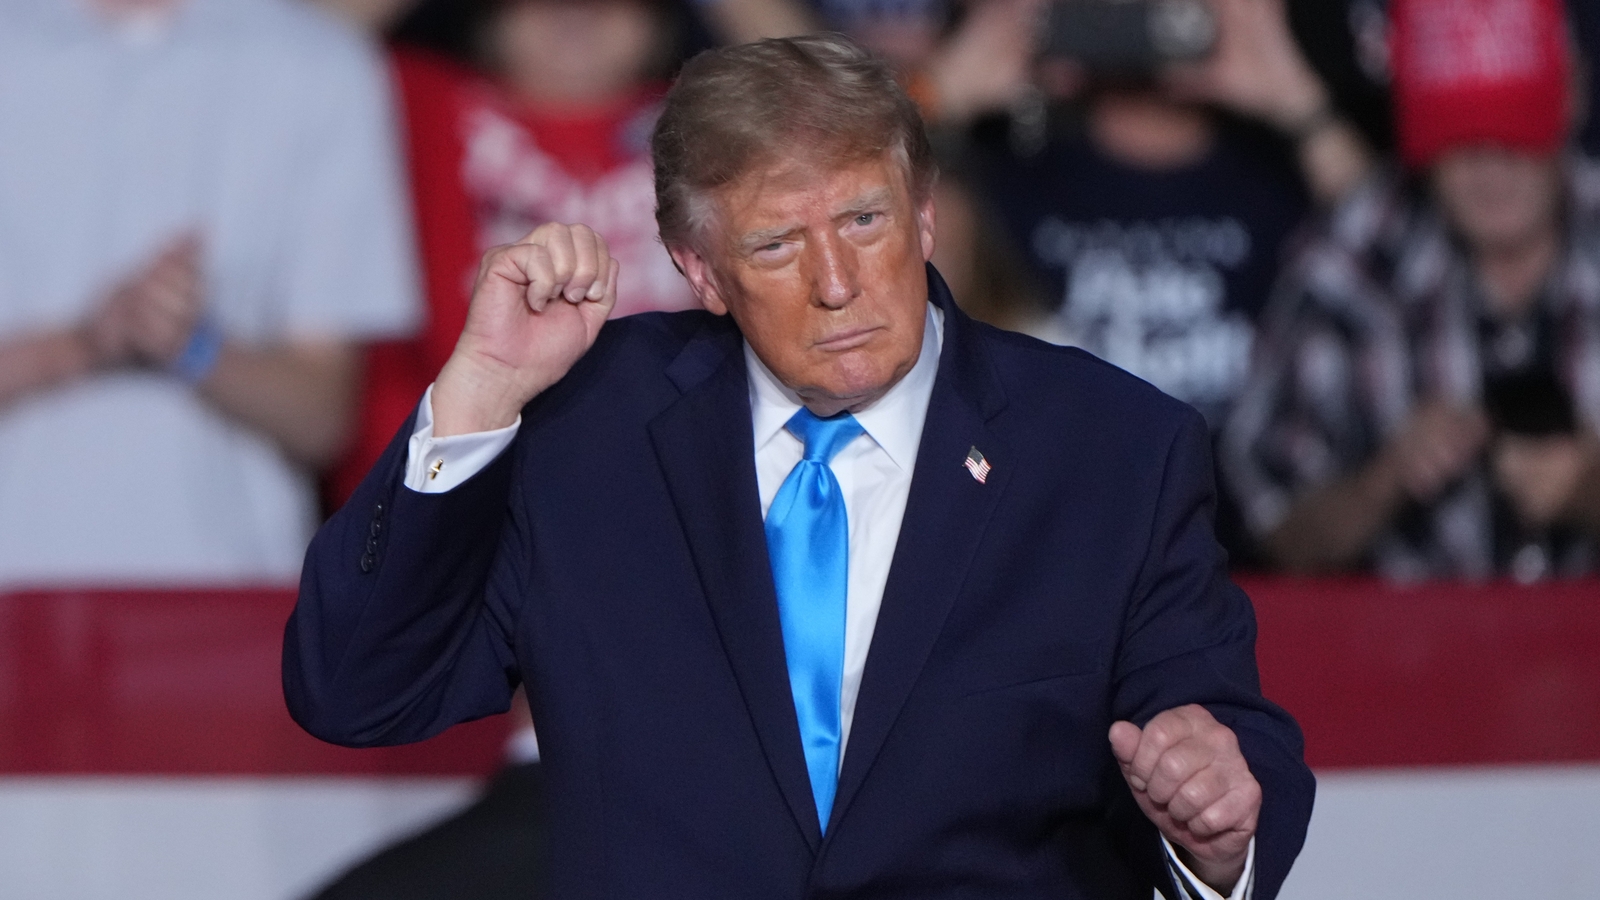
During a campaign rally in Nebraska on October 5, 2026, President Donald Trump suggested that Iran could 'take out' Los Angeles and San Diego, stating that the economic impact of the ongoing war with Iran is a 'small price to pay for keeping the world safe.' This remark drew immediate condemnation from California leaders, including Governor Gavin Newsom and San Diego Mayor Todd Gloria, who labeled Trump's comments as 'deranged and dangerous.' The White House later clarified that Trump was warning of potential threats from Iran, asserting that his administration's actions had prevented such attacks. The cities mentioned are significant due to their large populations and military installations. Trump's comments have raised concerns about the safety of American cities and the rhetoric used by a sitting president. As of now, there is no credible evidence that Iran possesses the capability to attack these cities directly.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (25)
Common questions
What did Trump say about Iran?
How did California officials respond?
Is there a real threat from Iran to US cities?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…