 News.Ycombinator
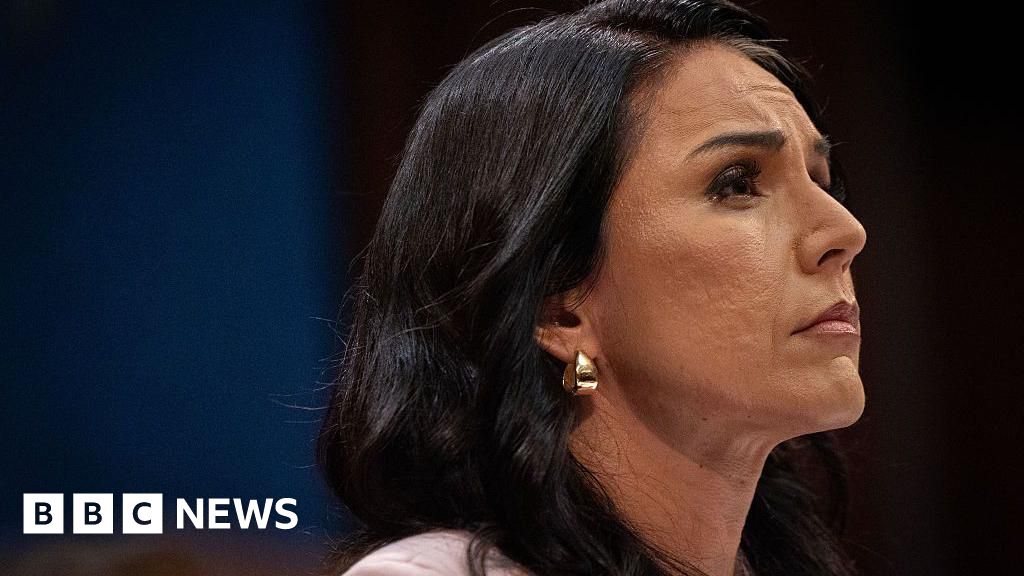
Tulsi Gabbard Resigns as Director of National Intelligence Amid Personal Crisis
Article Content

- •Tulsi Gabbard resigns as Director of National Intelligence due to her husband's cancer diagnosis.
- •President Trump praised Gabbard's performance and supported her decision to step down.
- •Gabbard's tenure included controversial alignment with Trump's intelligence agenda.
Tulsi Gabbard announced her resignation as the Director of National Intelligence, effective June 30, 2026, due to her husband's recent diagnosis of a rare form of bone cancer. In her resignation letter, she expressed gratitude for the opportunity to lead the Office of the Director of National Intelligence for the past 15 months. President Trump acknowledged her contributions and supported her decision to prioritize her husband's health. Gabbard's tenure was marked by her alignment with Trump's agenda, including efforts to investigate alleged politicization within the intelligence community. Despite her initial support, she faced challenges in maintaining influence within the administration as military actions escalated. Her departure is notable as she is the fourth cabinet official to leave the Trump administration in recent months.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…