 Hurriyetdailynews
Turkey and Armenia Sign MoU for Ani Bridge Restoration Amid Normalization Efforts
Article Content

- •Turkey and Armenia signed a MoU for the restoration of the Ani Bridge on May 4, 2026.
- •Vice President Yılmaz highlighted the significance of this agreement for regional peace and stability.
- •The project aims to enhance bilateral relations and serve as a model for conflict resolution.
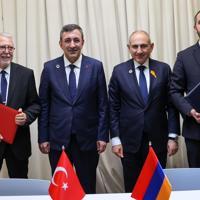
On May 4, 2026, Turkish Vice President Cevdet Yılmaz and Armenian Prime Minister Nikol Pashinyan signed a memorandum of understanding to restore the historic Ani Bridge, a significant step in the ongoing normalization process between Turkey and Armenia. This agreement was reached during the 8th European Political Community Summit held in Yerevan. Yılmaz emphasized the importance of this collaboration for regional stability and expressed hope that it would serve as an example for other conflict-affected regions. The memorandum aims to enhance transportation, customs, energy, and digital infrastructure connectivity between the two nations. Yılmaz also acknowledged contributions from Azerbaijan's President Ilham Aliyev in advancing this process. The restoration project is seen as a symbolic gesture towards lasting peace and trust in the South Caucasus. Preparations for the restoration are reportedly underway, with no remaining obstacles to starting the work soon.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…