 Straitstimes
UAE Beaches Closed Amid Oil Spill Linked to Iranian Tanker Attacks
Article Content

- •UAE has closed all beaches in Ras Al Khaimah due to an oil spill.
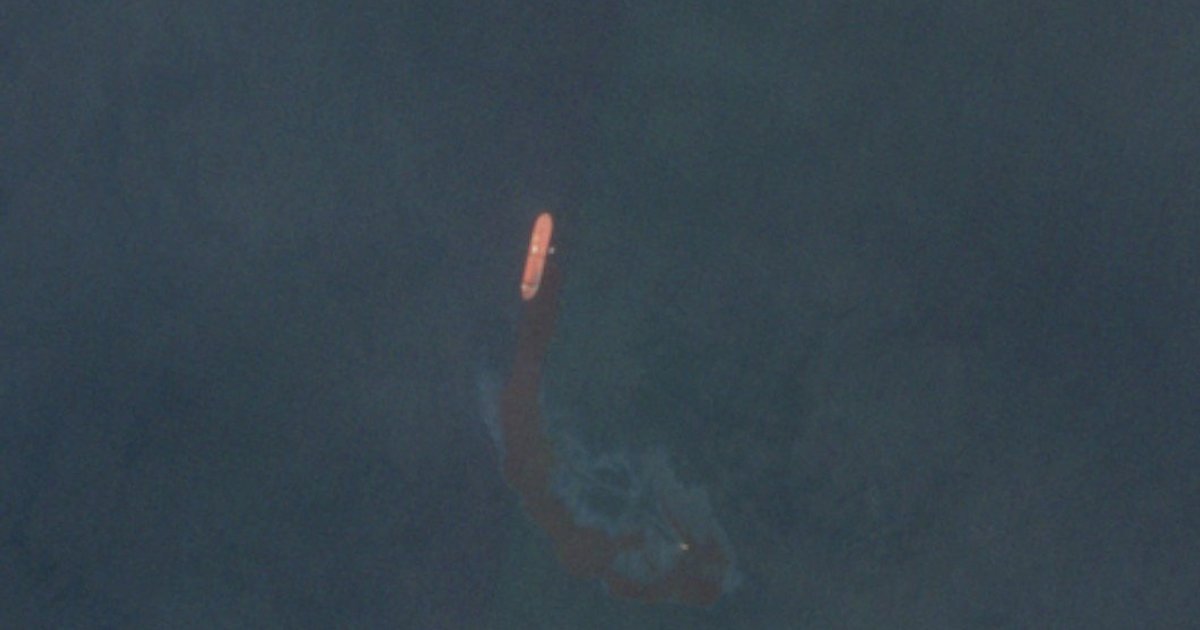
- •The spill is suspected to be linked to Iranian tanker strikes, particularly affecting the Gem No. 2.
- •Residents reported strong odors, but authorities confirmed no health risks.
The UAE confirmed an oil spill affecting beaches in Ras Al Khaimah, Umm Al Quwain, and Sharjah, likely linked to a tanker struck by Iran. The Ministry of Climate Change and Environment has closed all beaches in Ras Al Khaimah and advised fishermen to avoid affected areas due to strong odors reported by residents. The spill was first detected on October 19, with the UAE conducting environmental assessments and containment efforts. Iran has claimed responsibility for multiple vessel strikes in the region, contributing to heightened tensions amid ongoing conflicts. Despite the strong smells reported, the ministry stated there are no health risks. The source of the spill has not been officially confirmed, but it is suspected to be from the Taiwanese VLCC Gem No. 2, which was struck on October 9. Oil prices have surged, with Brent crude hovering around $115 per barrel as markets react to the situation.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What areas are affected by the oil spill?
Is there any health risk from the spill?
What actions are being taken to address the spill?
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Lazarus APT Launches Operation FlashHole Using AI and Post-Quantum Cryptography Kaspersky has identified a cyberespionage campaign, dubbed Operation FlashHole, attributed to the Lazarus APT group, active since July 2025. The campaign has targeted at least three organizations in South Korea's construction, software, and wire-communication sectors. Attack methods include spear-phishing emails…