 Mediaoffice.Abudhabi
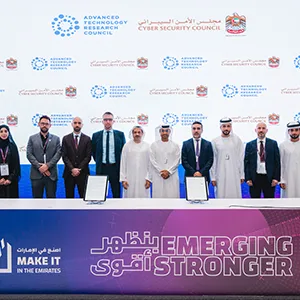
UAE Cyber Security Council and ATRC Partner for Quantum-Safe Security Transition
Article Content

- •UAE Cyber Security Council partners with ATRC to enhance quantum-safe security.
- •The initiative addresses rising global cyber threats and prepares for quantum computing impacts.
- •Deployment includes tools like the Crypto Discovery Tool for structured migration to quantum-resilient encryption.
On May 11, 2026, the UAE Cyber Security Council (CSC) signed an agreement with the Advanced Technology Research Council (ATRC) to advance the UAE's transition to quantum-safe security. This collaboration aims to enhance national resilience against evolving cyber threats amidst heightened global cyber risks. The partnership includes deploying cybersecurity solutions developed by the Technology Innovation Institute (TII) and VentureOne, focusing on post-quantum migration plans. Key tools include the Crypto Discovery Tool (CDT) and Entanglement-based Quantum Key Distribution (EQKD). The initiative is seen as a proactive measure to strengthen the UAE's digital infrastructure against future quantum computing threats. Both H.E. Dr. Mohamed Al Kuwaiti and H.E. Shahab Issa Abu Shahab emphasized the urgency of this transition for national security. The deployment will involve critical public and private sector entities, ensuring a structured migration path to quantum-resilient encryption standards.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…