 www.aol.co.uk
UK Government Launches Emergency Preparedness Campaign Amid Cyber Threats
Article Content

- •UK government launches a three-year campaign for emergency preparedness.
- •Citizens are advised to stockpile supplies for three days in case of disruptions.
- •Defence Secretary warns of increasing sophistication in cyber attacks from hostile states.
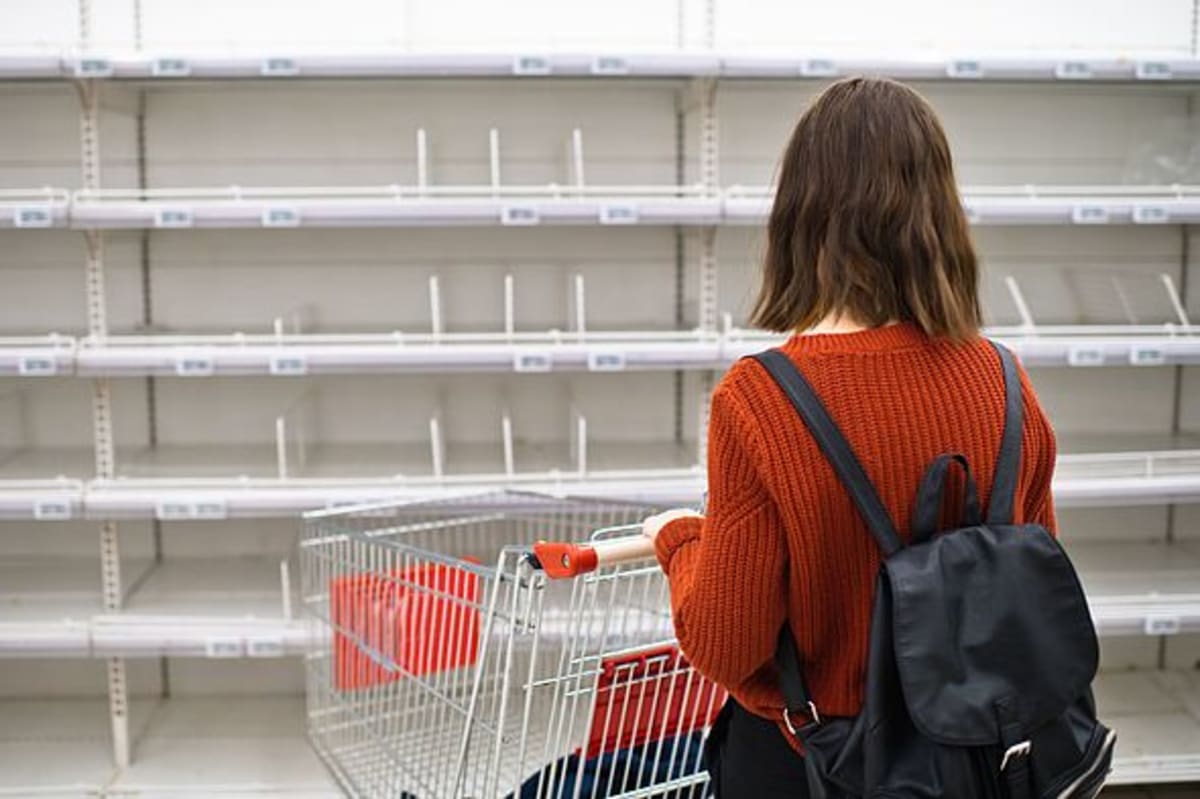
The UK government has initiated a 'Be Ready' campaign urging citizens to prepare for emergencies, including extreme weather and cyber attacks. Defence Secretary Wes Streeting emphasized the need for households and businesses to be ready for potential disruptions from hostile state actors. The campaign encourages stockpiling essential supplies for three days, including non-perishable food, water, and first aid kits. Streeting referred to the increasing sophistication of cyber attacks as part of hybrid warfare, which he termed 'state-terrorism.' The campaign aims to enhance national resilience over the next three years, with guidance shared through various media channels. MI5 director Ken McCallum has also highlighted the public's role in national preparedness, stating that everyone has a stake in resilience efforts.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What should I stockpile?
Why is this campaign being launched now?
How can I participate in the campaign?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…