 Theregister
UK Lawmakers Urge Termination of Palantir's NHS Contract Amid Vendor Lock-In Concerns
Article Content

- •UK lawmakers recommend ending Palantir's NHS contract due to vendor lock-in risks.
- •Palantir received £330 million for the NHS Federated Data Platform after controversial procurement.
- •Concerns raised about dependency on a few large tech companies in critical public services.
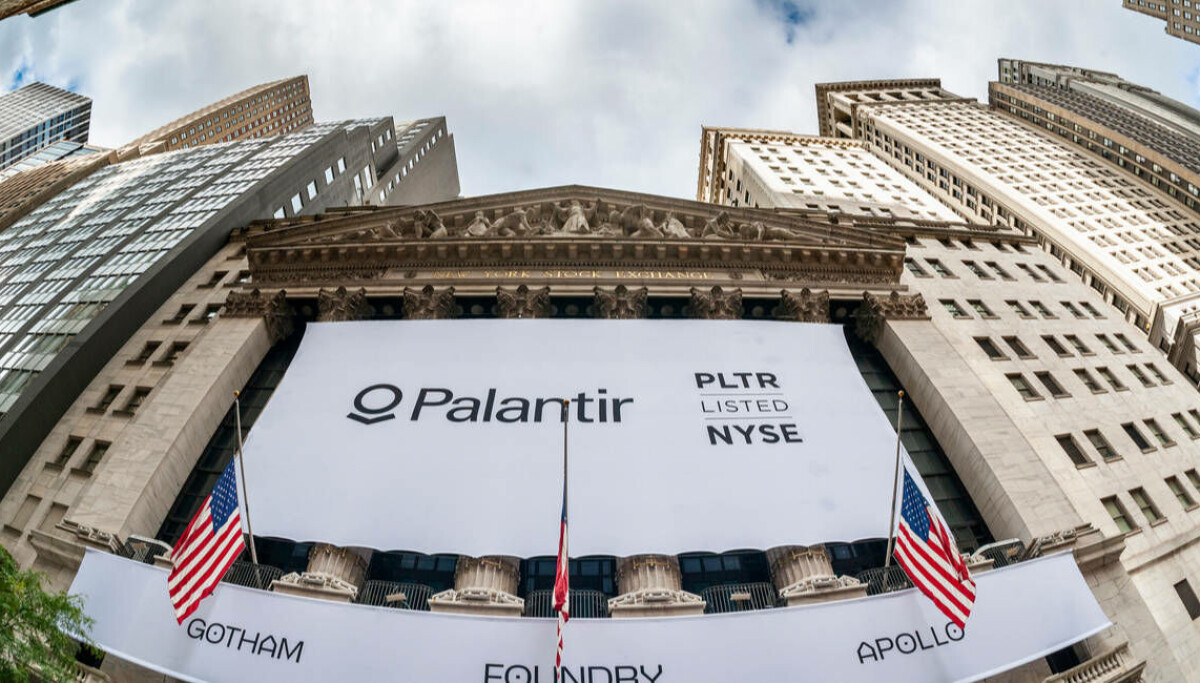
UK lawmakers have called for the government to end its contract with Palantir Technologies, citing concerns over vendor lock-in and the company's significant role in the NHS's Federated Data Platform (FDP). The Science Innovation and Technology Committee highlighted that Palantir's involvement poses risks to digital government plans and national security. The firm secured £330 million for the FDP contract in November 2023, following £60 million in Covid-era contracts awarded without competition. The committee emphasized the need for the government to diversify its suppliers and avoid dependencies on a few large tech companies. Dame Chi Onwurah MP stated that the current reliance on Palantir leaves the UK exposed, urging for technology sovereignty. The government is advised to utilize a break clause in the FDP contract set for February 2027 to seek alternatives. The situation reflects broader concerns about the implications of foreign tech firms in critical public sector roles.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (7)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…