 www.theguardian.com
UK Royal Navy Faces Resource Shortfalls Against Russian Threat in High North
Article Content

- •The UK Royal Navy is critically under-resourced to counter Russian threats in the High North.
- •All five Astute-class submarines were reportedly in dock this summer, limiting operational capacity.
- •The Defence Select Committee calls for immediate improvements to naval capabilities to deter Russian aggression.
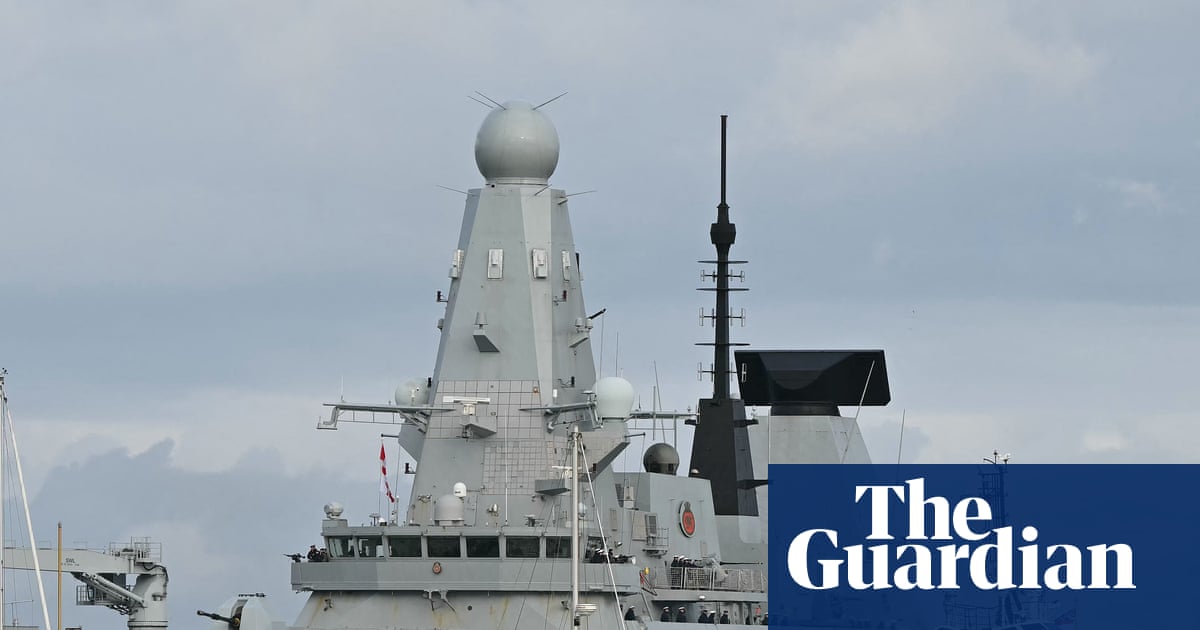
A report from the Defence Select Committee highlights critical shortfalls in the UK's naval capabilities in the High North, particularly against Russian aggression. The committee warns that the Royal Navy lacks sufficient submarines and warships, with all five Astute-class submarines reportedly in dock this summer. The ageing Type 23 frigates are also under-resourced, with only five operational against a requirement of eight. MPs emphasize the need for 'dramatic progress' in naval resources by the end of the decade to deter Russian activities in strategically significant Arctic waters. The report cites increased Russian interest in energy pipelines and undersea cables as a growing concern. Defence Secretary's recent visit to Iceland underscored the UK's commitment to tracking Russian submarine activity. The Ministry of Defence acknowledges the threat posed by Russia but has not detailed specific plans to address these shortfalls.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What specific naval resources are lacking?
What is the current status of the Astute-class submarines?
What actions is the UK taking to address these shortfalls?
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Lazarus APT Launches Operation FlashHole Using AI and Post-Quantum Cryptography Kaspersky has identified a cyberespionage campaign, dubbed Operation FlashHole, attributed to the Lazarus APT group, active since July 2025. The campaign has targeted at least three organizations in South Korea's construction, software, and wire-communication sectors. Attack methods include spear-phishing emails…