 www.kyivpost.com
Ukraine Claims Major Hack of Russian Aerospace Firm Tupolev
Article Content

- •Ukraine's HUR hacked Tupolev, stealing 4.4 GB of classified data.
- •The breach included sensitive internal communications and personal data of staff.
- •Ukrainian operatives defaced Tupolev's website as part of the cyber operation.
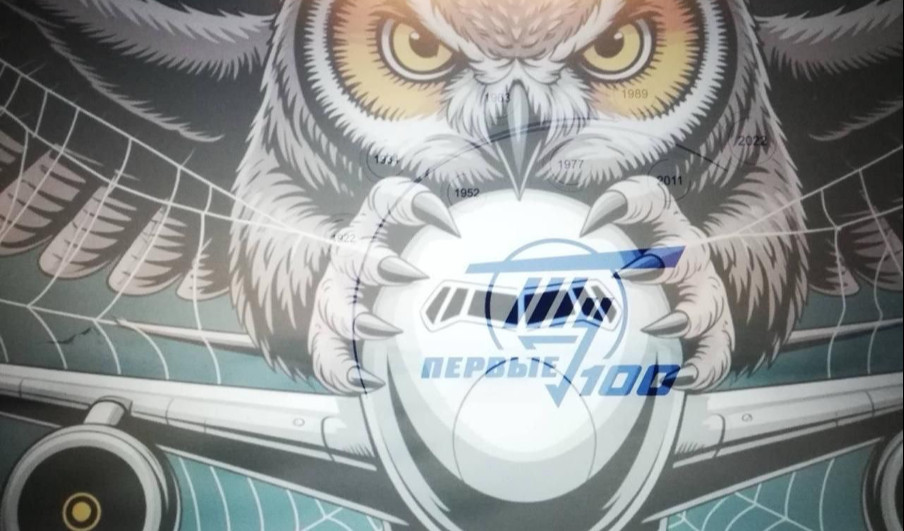
Ukraine's Military Intelligence (HUR) claims to have hacked the Russian aerospace company Tupolev, stealing 4.4 gigabytes of classified data. The breach includes internal communications, personal data of employees, and procurement documents. The operation reportedly lasted a significant period, allowing for extensive data collection. Ukrainian operatives also defaced Tupolev's website, replacing its main page with an image of an owl clutching an aircraft. This attack follows previous breaches of Russian defense agencies and highlights ongoing cyber operations against Russia's military-industrial complex. The stolen data is expected to have a considerable impact on Russian strategic aviation operations. HUR has been systematically targeting Russian military entities since the escalation of the conflict in 2022.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Commonwealth Of Independent States Institute in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…
 Volt Typhoon's Silent Train Network Targets US Critical Infrastructure The Chinese state-sponsored hacking group Volt Typhoon has been linked to a covert network called Silent Train, which has exploited at least four zero-day vulnerabilities over three years. This network utilizes rapidly rotating chains of compromised SOHO routers, IoT devices, and enterprise infrastructure to access…