 Unn.Ua
Ukraine Enhances FBI Cooperation to Combat Cybercrime Amid Russian Aggression
Article Content

- •Ukraine is intensifying cooperation with the FBI to combat cybercrime and gather evidence against Russia.
- •The focus includes digital forensics and prosecuting cybercriminals involved in ransomware and data theft.
- •U.S. technical support is deemed crucial for enhancing Ukraine's capabilities in digital evidence collection.
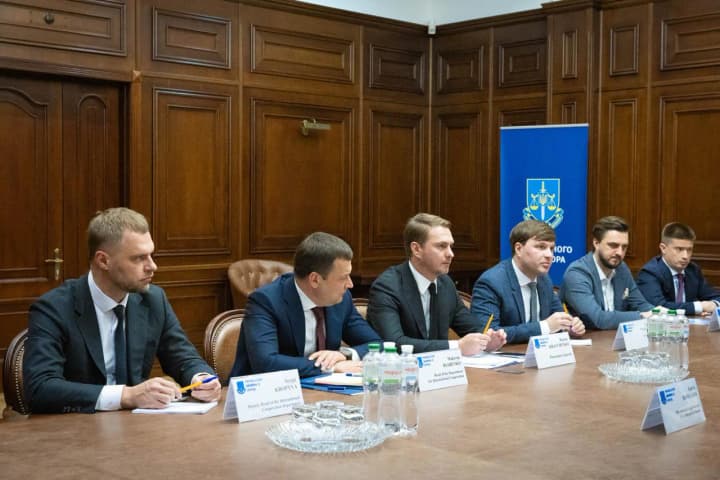
On June 5, 2026, Ukraine's Prosecutor General Ruslan Kravchenko announced a deepened collaboration with the FBI's cyber division to combat international cybercrimes and gather evidence of Russian aggression. The meeting included key FBI officials, focusing on digital forensics and the prosecution of cybercriminals. Kravchenko highlighted the importance of building a robust evidentiary base against Russia's military actions, emphasizing the need for U.S. technical support in digital data analysis. He noted that Ukraine is responsive to U.S. legal assistance requests, with ongoing cases involving ransomware and personal data theft. The cooperation aims to enhance joint operations and information exchange between the two nations. The meeting concluded with FBI awards presented to Ukrainian prosecutors, signifying the practical outcomes of their collaboration.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…