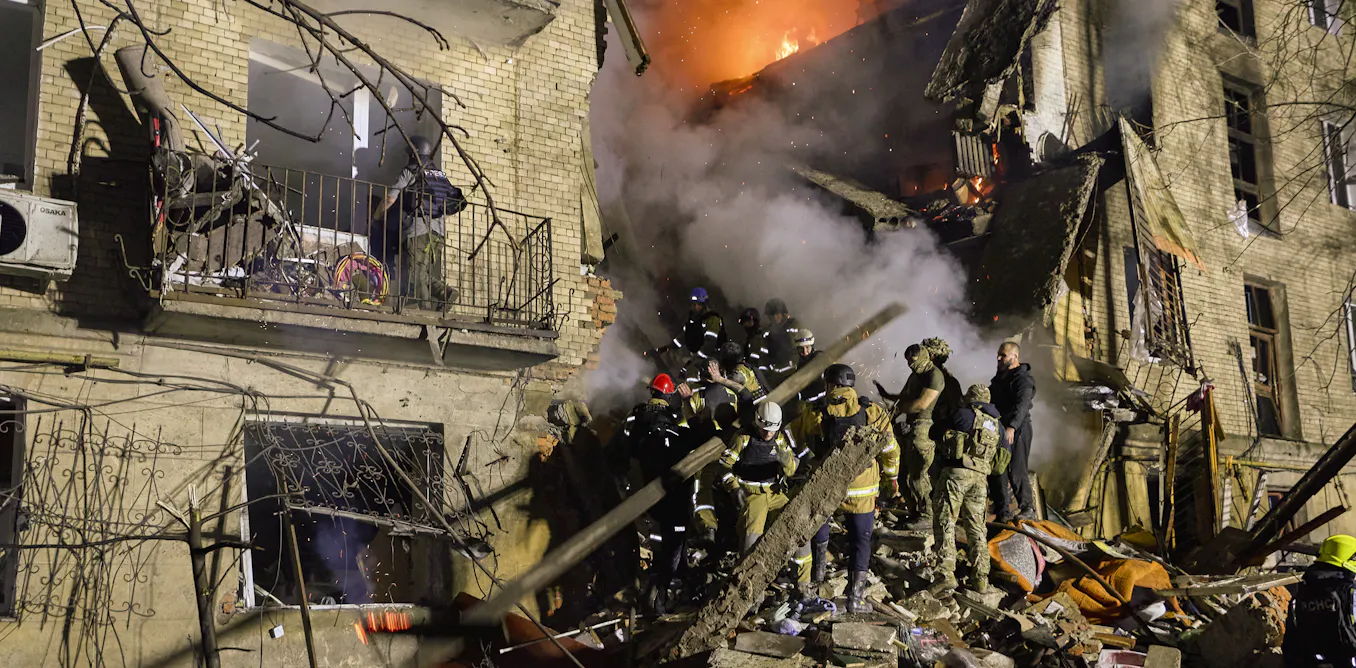 Theconversation
Ukraine Resumes Strikes on Russian Oil Refineries Amid Escalating Attacks
Article Content

- •Zelensky resumes strikes on Russian oil refineries after a brief pause due to U.S. pressure.
- •Russia has intensified attacks on Ukrainian civilian infrastructure, including energy facilities.
- •U.S. intelligence-sharing has reportedly been reduced, impacting Ukraine's military operations.
Ukrainian President Volodymyr Zelensky announced the resumption of strikes on Russian oil refineries, citing a lack of U.S. support and continued Russian attacks on Ukrainian energy infrastructure. Zelensky had previously limited these strikes for three days at the request of the U.S., which he claims has since withdrawn crucial intelligence-sharing. Following the announcement of a proposed 'energy ceasefire' by U.S. President Donald Trump, Russia intensified its attacks on Ukrainian power facilities, leaving hundreds of thousands without power. Zelensky expressed feelings of betrayal by the U.S. and stated that Ukraine would only halt strikes on Russian oil infrastructure if provided with more Patriot air defense missiles. The ongoing conflict has seen a significant increase in Russian strikes targeting civilian infrastructure, including energy and transport systems, exacerbating the humanitarian crisis in Ukraine.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What triggered the resumption of strikes?
How has Russia responded to the ceasefire proposal?
What does Zelensky need from the U.S. now?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…