 United24Media
Ukraine Strikes Key Russian Plant for Missile Components
Article Content

- •Ukraine targeted the Energiya plant, vital for Russian missile production.
- •The strike utilized Storm Shadow cruise missiles supplied by the UK.
- •This attack is part of a broader strategy to disrupt Russian military capabilities.
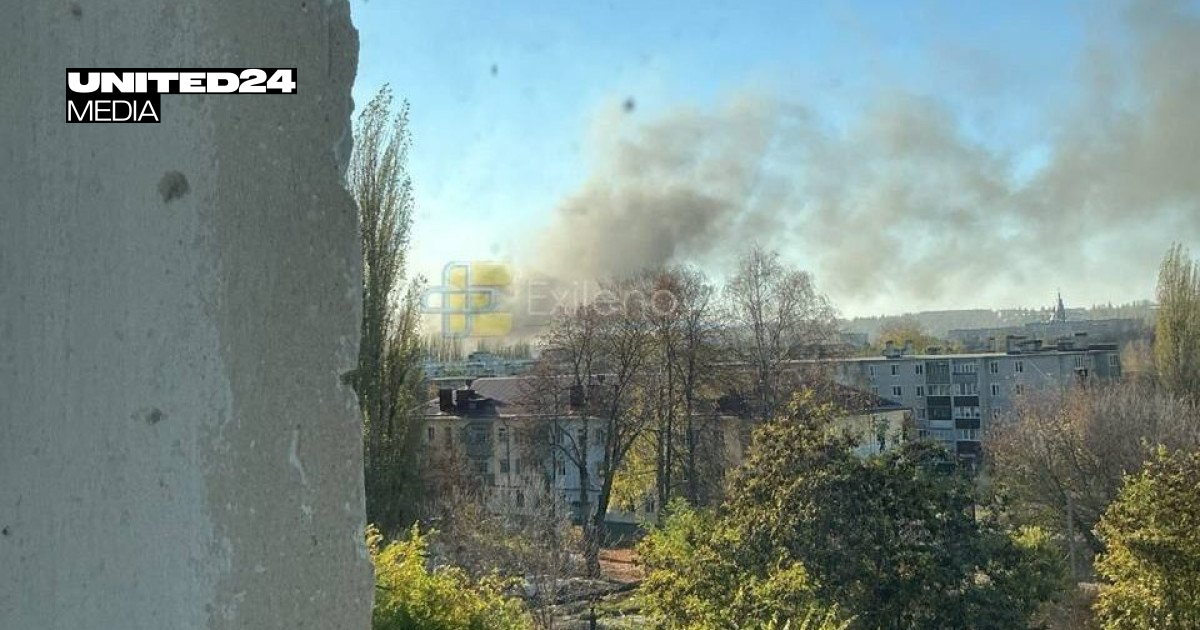
On October 25, 2026, Ukraine reportedly struck the Energiya plant in Yelets, Russia, using UK-supplied Storm Shadow cruise missiles. The plant is a crucial supplier of batteries and power systems for Russian missile systems, including Iskander and Kinzhal missiles. Footage from the OSINT channel Exilenova+ showed multiple missile impacts, resulting in significant explosions and smoke. The regional governor confirmed the attack on the industrial zone, emphasizing the plant's strategic importance to Russia's defense industry. This strike follows a similar attack on the Proton electronics plant in Oryol, which occurred two days earlier. The extent of damage and potential impact on production at the Energiya plant remains unverified. The facility's products are integral to many Russian military operations against Ukraine.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Energia in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is the significance of the Energiya plant?
What type of missiles were used in the strike?
What are the implications of this attack?
Continue Reading
 .NET Vulnerability CVE-2026-111497 Requires Immediate Action On October 25, 2026, Microsoft released out-of-band security updates for.NET addressing CVE-2026-111497, a vulnerability in the Brotli decompression algorithm that allows unauthorized attackers to elevate privileges over a network. The flaw affects.NET versions 8, 9, 10, and 11, particularly in applications that…
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…