 Pravda.Ua
Ukraine Strikes Russian Drone Plant in Taganrog, Reducing UAV Production Capacity
Article Content

- •Ukrainian forces struck the Atlant-Aero drone plant in Taganrog on April 19, 2026.
- •The strike utilized Neptune cruise missiles, targeting a facility critical for UAV production.
- •The operation is part of Ukraine's broader strategy to reduce Russian military capabilities.
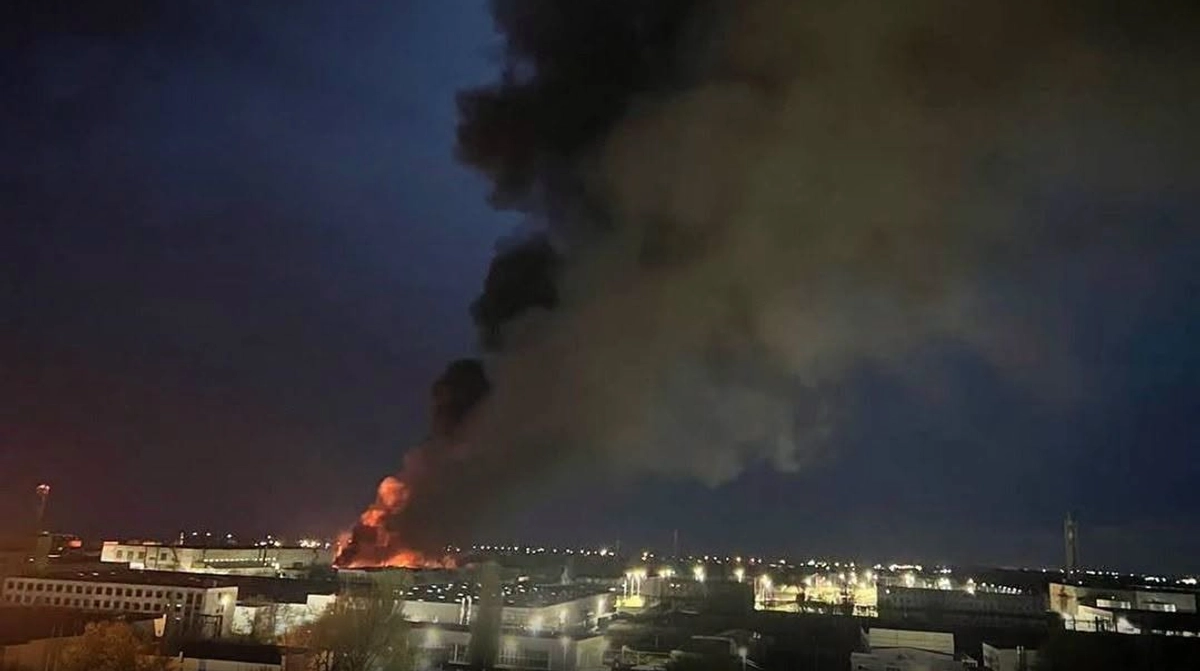
On April 19, 2026, Ukrainian forces targeted the Atlant-Aero drone production facility in Taganrog, Russia, using Neptune cruise missiles. This facility is known for developing Molniya and Orion UAVs, which are integral to the Russian military's drone operations. The strike resulted in a fire and is expected to significantly diminish Russia's ability to produce drones capable of attacking Ukrainian civilian infrastructure. In addition to the drone plant, Ukrainian forces also struck multiple logistical and ammunition sites in occupied territories, including Trudove and Mariupol. The Ukrainian military reported that the strike on Taganrog is part of ongoing efforts to weaken Russian military capabilities. Russian authorities reported minor injuries from the strikes, but the full extent of the damage is still being assessed. The attack marks a continuation of Ukraine's strategy to disrupt Russian military supply chains and production capabilities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (9)
Following this threat?
Track orion and Atlant Aero in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…
 Volt Typhoon's Silent Train Network Targets US Critical Infrastructure The Chinese state-sponsored hacking group Volt Typhoon has been linked to a covert network called Silent Train, which has exploited at least four zero-day vulnerabilities over three years. This network utilizes rapidly rotating chains of compromised SOHO routers, IoT devices, and enterprise infrastructure to access…