 Newsukraine.Rbc.Ua
Ukrainian Cyber Exercise Simulates Russian Tactics Against NATO
Article Content

- •Ukrainian specialists simulated Russian tactics in a NATO cyber exercise.
- •The exercise involved three crisis scenarios, including a cyberattack on a power grid.
- •Ukrainian participants narrowly lost, showcasing advanced skills in AI and disinformation.
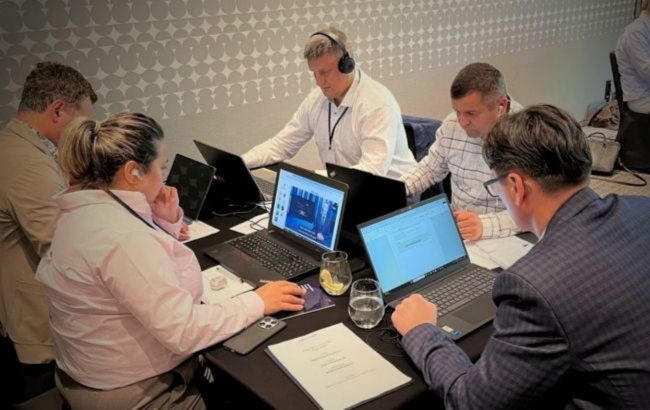
Ukrainian specialists participated in a NATO cyber exercise in Bydgoszcz, Poland, simulating a cyberattack from a fictional adversary, Karti, against the fictional country of Perantsa. The exercise tested NATO's readiness to counter disinformation campaigns similar to those faced by Ukraine since the onset of the Russian invasion. Over three days, scenarios included a power grid cyberattack, a major flood, and a banking system breach. Ukrainian participants, portraying Karti, utilized AI-generated social media messages to undermine Perantsa's government, which responded with calls for unity. The Ukrainian team narrowly lost in two of the three scenarios, demonstrating advanced tactics and creativity. The exercise, funded by the German military, involved personnel from Ukraine's Armed Forces and intelligence agencies, enhancing interoperability with NATO. Experts noted the limitations of simulations in fully replicating real-world conditions. The event highlights the ongoing importance of cyber readiness amid geopolitical tensions.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (9)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…