 Arkansasonline
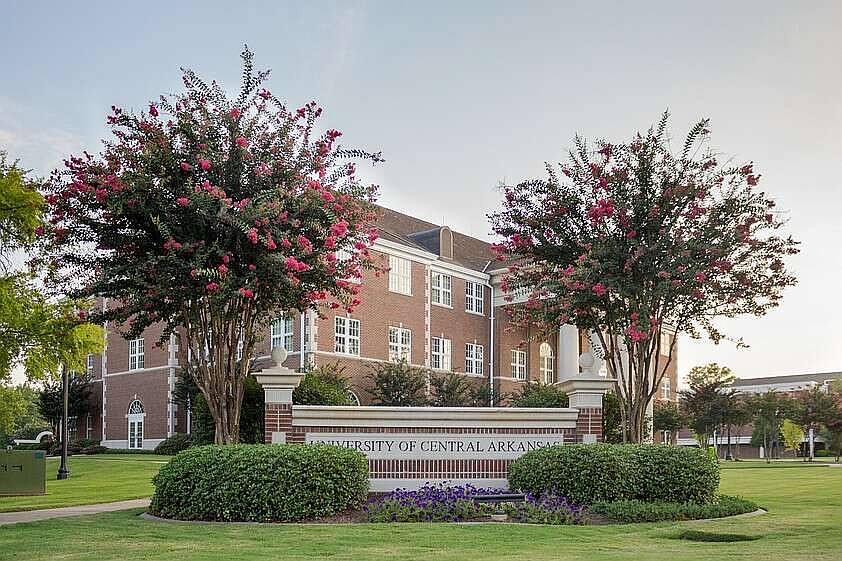
University of Central Arkansas Reports Data Breach Exposing Email Addresses
Article Content

- •Data breach at University of Central Arkansas Community Care Clinic exposed email addresses.
- •Unauthorized access occurred between September 4 and September 28, 2026.
- •No medical records or financial information were compromised.
The University of Central Arkansas disclosed a data breach at its Community Care Clinic that occurred between September 4 and September 28, 2026. Unauthorized access to one of the clinic's IT systems was detected on September 28, leading to the exposure of an undisclosed number of email addresses. Medical records, credit card information, and financial account numbers were not compromised. The clinic has since secured its systems and enhanced security measures, including staff retraining on cybersecurity awareness. The incident may result in phishing attempts targeting affected email addresses. The breach was reported to the U.S. Department of Health and Human Services as required by law. This incident aligns with a broader trend of increasing ransomware attacks against educational institutions, with a reported 88% rise in such attacks from the second to third quarter of 2026.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Community Care Clinic in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What information was compromised?
What actions should affected individuals take?
How did the breach occur?
Continue Reading
 Binance Hack: $6.3 Billion Stolen in Largest Crypto Heist On October 29, 2026, Binance, the world's largest cryptocurrency exchange, reported a major security incident involving an estimated $6.3 billion in stolen funds. The attack was attributed to a compromised laptop belonging to a DevOps engineer, allowing unauthorized withdrawal transactions. Approximately $3 billion in…
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…