 news.bitcoin.com
Uranium Finance Hacker Convicted for $55 Million Theft
Article Content

- •Jonathan Spalletta was convicted of stealing nearly $55 million from Uranium Finance.
- •The attacks occurred in April 2021, exploiting flaws in smart contracts.
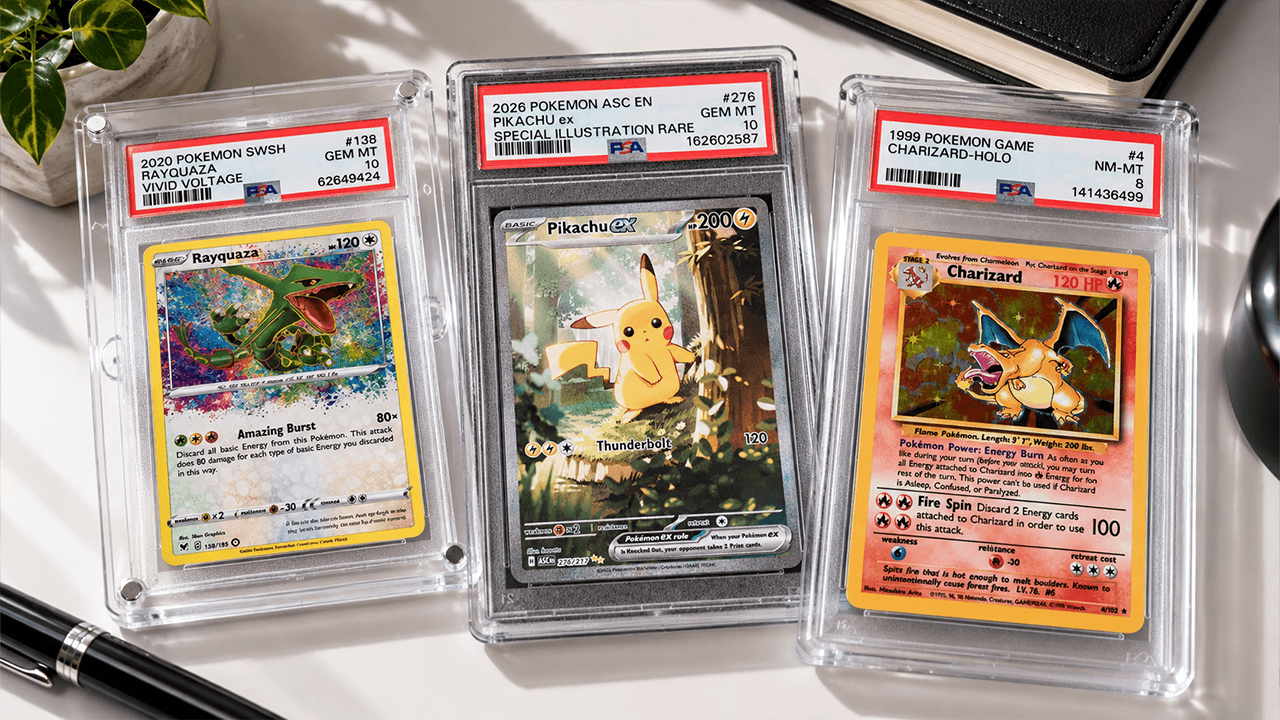
- •Spalletta laundered funds through Tornado Cash and purchased rare collectibles.
Jonathan Spalletta, a cybersecurity consultant, was convicted by a New York jury for stealing nearly $55 million from Uranium Finance through two attacks in April 2021. The first attack exploited a flaw in the rewards mechanism, netting approximately $1.4 million, while the second attack targeted 26 liquidity pools, resulting in $53.3 million in losses. Spalletta laundered the stolen funds using Tornado Cash and spent significant amounts on rare collectibles, including Pokémon and Magic: The Gathering cards. The jury deliberated for over two hours before reaching a verdict on October 7, 2026. He faces a maximum of 20 years for money laundering and 10 years for computer fraud, with sentencing scheduled for February 16, 2027. Federal authorities seized $31 million in cryptocurrency and collectibles tied to the theft. Spalletta's defense argued that he exploited publicly available smart contract functions rather than hacking.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track Uranium Finance in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What was the total amount stolen?
What were the charges against Spalletta?
How did Spalletta launder the stolen funds?
Continue Reading
 Critical Citrix NetScaler Vulnerabilities Actively Exploited in Finland The National Cyber Security Centre Finland (NCSC-FI) issued an alert regarding critical vulnerabilities in Citrix NetScaler ADC and Gateway products, specifically CVE-2026-88771 and CVE-2026-88772, which are being actively exploited in Finland. These vulnerabilities allow attackers to execute remote code without…
 Critical Authentication Bypass in Rejetto HFS Exploited Within 24 Hours Anthropic's Mythos model identified a critical authentication bypass in Rejetto HTTP File Server (HFS), tracked as CVE-2026-61500, allowing remote code execution. Discovered by Horizon3 researcher Zach Hanley, the flaw was revealed on September 27, 2026, and exploitation began within 24 hours, with attacks traced to…